WordPress 7 AI features vs AI Agent for WordPress: What’s built-in and what needs an agent

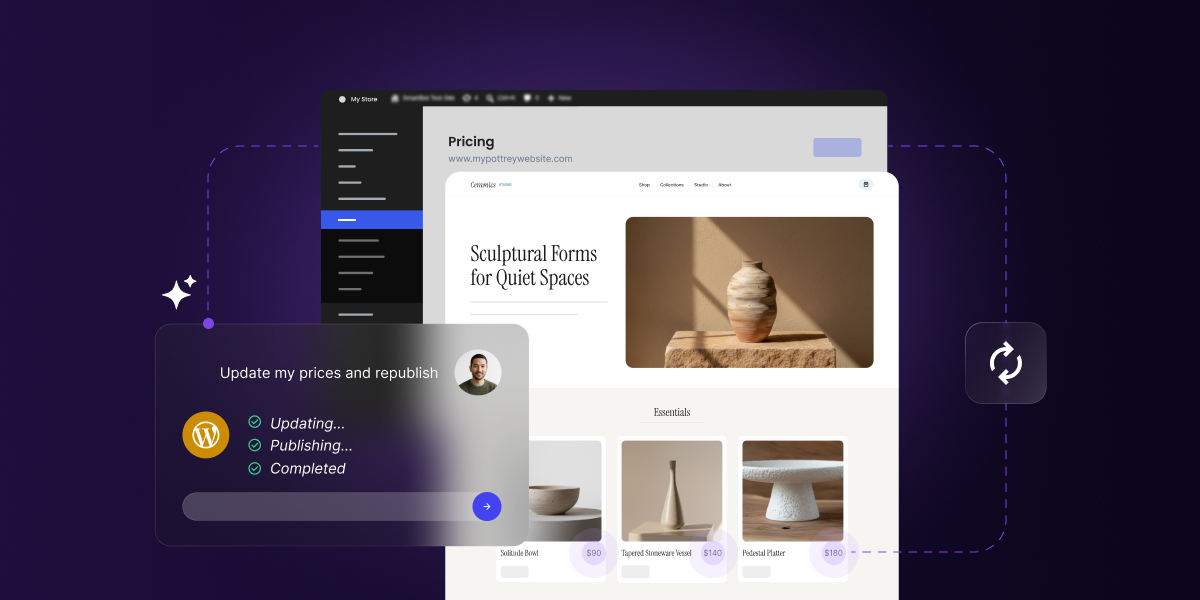
A digital graphic depicting AI-assisted e-commerce price updates and automated site publishing on a dark purple background. In the foreground, a floating translucent UI window displays a user prompt, "Update my prices and republish," alongside green checkmarks for "Updating...," "Publishing...," and "Completed" next to a WordPress logo. In the background, a ceramics website preview showcases updated item prices under an "Essentials" section, featuring the "Solitude Bowl" at "$90," "Tapered Stoneware Vessel" at "$140," and "Pedestal Platter" at "$180."

You’ve probably heard that WordPress 7 brings AI into WordPress itself. But if you upgrade to WordPress 7.0 or later and go looking for AI features, you won’t find any waiting for you. What arrived is a shared infrastructure for connecting AI to your site rather than features, so on its own it changes nothing you can see in your dashboard. 

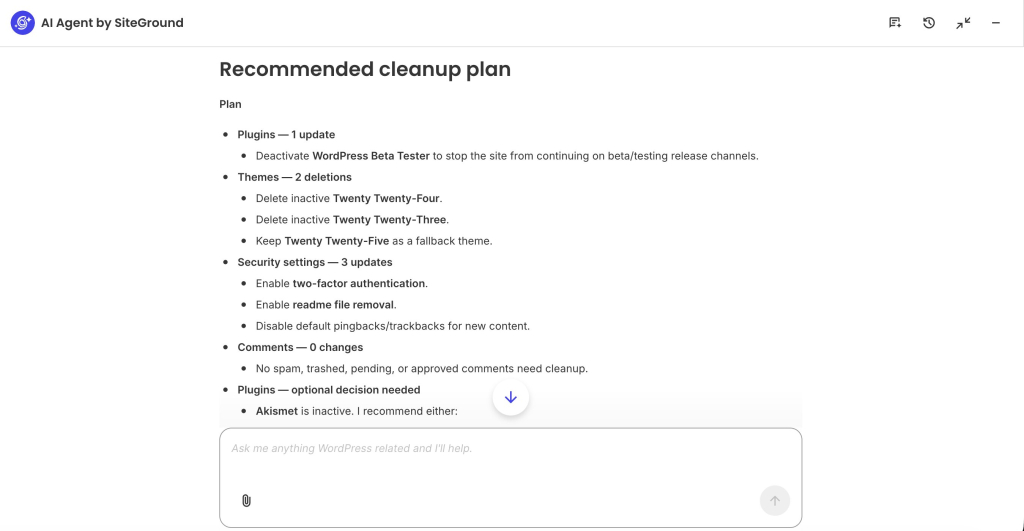
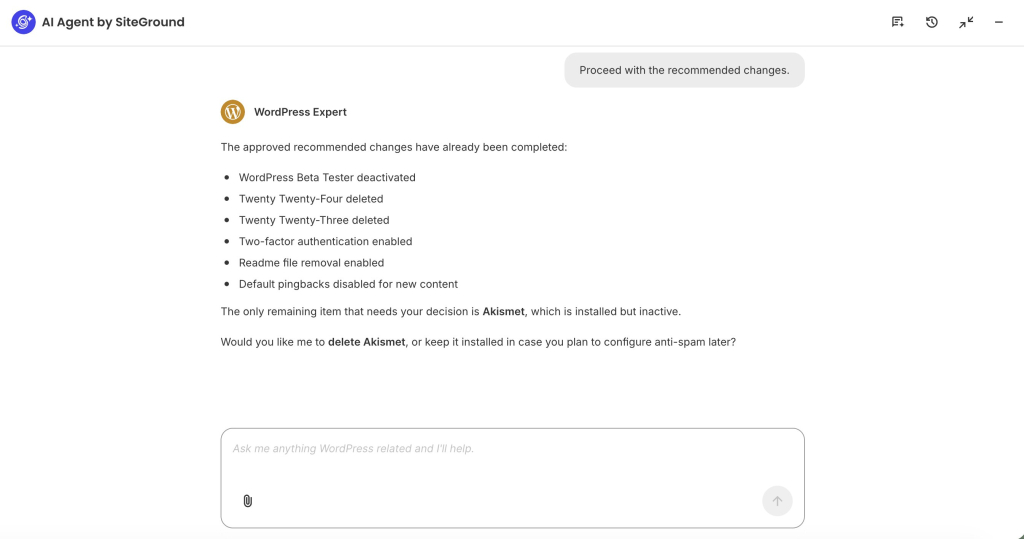
Something has to sit on top of that infrastructure, and the most capable option available today is a specialized AI Agent for WordPress: a tool that connects to your site, understands what’s on it, and carries out work across your dashboard when you ask in plain language. Comparing WordPress 7 AI features vs an AI Agent for WordPress is a question of what the platform now gives you and how much further an AI Agent takes it.

Key takeaways:

  • WordPress 7 introduced shared AI infrastructure, but no user-facing AI features out of the box. Your dashboard looks the same after the update. What arrived is a connection system that other tools build on.
  • You connect an AI provider once, in Settings > Connectors. Compatible plugins then share that connection, instead of you pasting the same API key into every plugin’s settings.
  • Most providers charge you directly for what you use. You create an account with OpenAI, Google, or Anthropic, generate an API key, and the usage is billed to you.
  • WordPress 7 AI features vs AI Agent for WordPress is a question of reach. The infrastructure connects AI to your site, while an agent like SiteGround’s AI Agent for WordPress is what actually carries out work across it through a simple chat that follows you between screens.

What WordPress 7 actually added

Until WordPress 7, there was no common system for how AI worked inside WordPress. If you wanted AI features, every plugin handled it differently. An AI writing tool connected to one service with its own API key (a unique credential that lets a plugin communicate with an AI provider). An AI SEO plugin connected to a different service with a different key, while an image generator needed a third setup. Run all three, and you were managing three sets of credentials in three settings panels, often paying for overlapping subscriptions, and none of those tools could share anything with each other. 

WordPress 7.0 (the first version of WordPress 7, which was recently followed by WordPress 7.1) solved that by building a shared AI layer directly into core (the base software that powers every WordPress site).

The new WordPress 7.0 AI Client is the part that standardizes how plugins request AI work, so a plugin now asks WordPress, and WordPress routes the request to whichever provider you’ve connected. The WordPress Connectors API powers the Connectors screen, where you manage those provider credentials in one place. And the WordPress Abilities API keeps a structured register of what your site itself can do, such as publishing a post or updating a product, so AI tools can discover what’s possible. 

To get the full picture, read our guide to how AI works in WordPress 7.0.

What happens the moment you upgrade

The only visible change for you is the new WordPress Connectors screen under Settings, where WordPress AI provider setup now happens. Open it, and you’ll find cards for the three providers WordPress features by default: OpenAI, Google Gemini, and Anthropic Claude. Each one needs an API key (a unique credential that lets your site communicate with that provider). To get one, you create an account on the provider’s website, go to their API or developer section, generate a key, and paste it into the card. From that point, whatever AI work happens on your site is billed to that account.

Beyond OpenAI, Google Gemini, and Anthropic Claude, the system is open, and community-built providers can be added from the same page, each requiring you to install its provider plugin and enter your own key. You may also see Akismet listed there, which isn’t an AI provider at all. The Connectors screen stores credentials for external services generally, and anti-spam was the first non-AI example WordPress added.

Pro tip: set a spending limit. AI providers charge per token, and WordPress has no spending cap of its own, so nothing on your site stops the meter once a connection is live. A plugin making frequent background calls, or one busy month of content, can multiply a bill before it shows up on a statement. OpenAI and Anthropic both let you set a hard monthly cap in your account settings, which takes about a minute. Google’s billing runs through Google Cloud, where the default is a budget alert that emails you rather than a limit that stops anything, so check what you’ve actually set there.

If your WordPress site is hosted on SiteGround, there’s a fourth option on that page. SiteGround AI is already installed and connected as an AI provider, with authentication handled automatically through your SiteGround account, so it appears in Connectors as already active with no API key to paste.
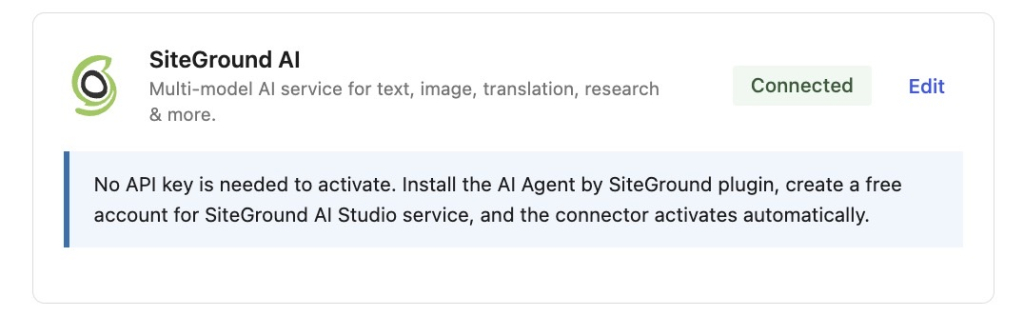
SiteGround AI connector card showing a "Connected" status badge and Edit link, with a note that no API key is needed — install the AI Agent by SiteGround plugin and create a free SiteGround AI Studio account to activate automatically.

The six layers between an AI model and a finished task

Let’s illustrate how you can use AI in WordPress 7 and above with an example of a simple task. Say you want to add alt text to an image you have in your WordPress Media Library, and you want to use AI to generate it right into the editor. Six things have to be in place:

What’s neededWhat it meansWhere it comes from
An AI modelThe thing that looks at a photo and writes the descriptionAn outside provider such as OpenAI, Google, or Anthropic
A connection to itPermission for your site to send requests to that providerYou, through Settings > Connectors, with your own account and API key
A standard way to askPlugins requesting AI work without writing code for each providerWordPress core, since 7.0. This is the AI Client, and it works invisibly
Permission to actWriting the result into the Alt text field, rather than only showing you wordsThe Abilities API in core, plus whatever your plugins have registered
Somewhere to ask fromA button, a screen, or a chat where you make the requestNothing in core. WordPress 7 ships no user-facing AI features at all
The finished jobYour image with alt text saved on itOnly if all five above are in place for this particular task

Everything on that list apart from the finished job is either supplied by WordPress core or connected by you in a few minutes. What core deliberately doesn’t include is anywhere to make the request, because the platform’s job is to provide the connection and leave the tools to everyone else.

Pro tip: check what your provider can’t do before you pick it. Not every provider handles every kind of request. For example, Anthropic Claude generates text but not images, so if you connect Claude alone and a plugin asks for an image, WordPress will look for another provider that can handle it and find nothing. The routing between providers is automatic, but only if you’ve connected a second one that covers the gap. If you want both text and images, that means two accounts, two API keys, and two bills to watch.

WordPress 7 AI features vs AI Agent for WordPress, layer by layer

So WordPress 7 AI features become usable once you install AI plugins that have adapted to the new infrastructure. As we found in our 2026 report on AI in WordPress for small businesses, most of those plugins focus on generating content inside the editor: titles, excerpts, alt text, images, summaries.

What extends WordPress 7’s AI features much further, and makes fuller use of them, is a specialized AI agent like SiteGround’s AI Agent for WordPress that can generate content and also handle actual WordPress management. Instead of clicking through admin screens, you describe what you need in a chat that sits in your dashboard, and it transforms tasks that typically take hours of manual admin work into minutes of conversation. Here’s how the two compare:

WordPress 7 on its ownAI Agent for WordPress
What it isInfrastructure: a shared way for plugins to reach AI providersA WordPress AI management assistant that reads and acts on your site, delivered as a chat in your WordPress admin
What you get after setupA connected provider, and plugins that can use itA chat you can ask for work, available on every admin screen
What it can do for youNothing directly. It enables other toolsContent, plugins, themes, products, orders, users, site structure, and bulk changes
How you use itYou configure the connection. Compatible plugins use it on your behalfYou describe what you want in plain language
SetupA provider account, an API key, and that provider’s plugin activatedUp and running for SiteGround-hosted sites. For sites hosted elsewhere, it’s a lightweight plugin 
Who pays for AI usageYou, directly to the provider you connectedCovered by your AI Studio workspace, with usage visible in one place
Works onWordPress 7.0 and later Any WordPress site, with the Connectors entry appearing on 7.0 and later

Do you need an AI Agent for WordPress after WordPress 7?

It depends on what you want the AI to do. The useful way to decide is by the job rather than the product label.

When WordPress 7 and AI plugins are enough

If your goals are highly focused and repeatable, standard AI plugins are often all you need. In-editor tools like Jetpack AI are excellent for drafting and rewriting copy right where you type, while established SEO tools like Yoast and Rank Math are perfect for page-by-page metadata, schema suggestions, and content scoring.

Stick with AI plugins working with WordPress 7’s infrastructure if:

  • You’re comfortable running an AI provider account. For developers and agencies, choosing the model and controlling spending at the provider level is a feature rather than a cost.
  • You only need depth in a single, isolated area. If your primary AI need is a dedicated customer support chatbot to capture leads on your homepage, or a tool to optimize an individual post’s SEO, a purpose-built single-function plugin is the right tool for the job.
  • You already have tools that work. Our guide to choosing between AI plugins and AI agents makes the case that these categories aren’t exclusive, and many growing sites end up running both.

When you need a WordPress AI management assistant instead

Content creation is only a fraction of running a website. For small businesses, the real time-sink is the endless operational overhead: managing product catalogs, processing store orders, auditing user permissions, and keeping multiple domains synchronized. Because these tasks happen entirely outside the post editor, standard in-editor AI content generators cannot help you.

A site-connected management agent like SiteGround’s AI Agent for WordPress is built specifically for operations, making it the perfect fit if:

  • You want to bypass the complexity of API keys and provider billing. Juggling developer dashboards for multiple AI models is an administrative headache. With the AI Agent for WordPress, there are no raw API keys to generate, copy, or maintain. All usage of leading models is consolidated under a single subscription
  • You need system-wide operations, not just text generation. Standard AI plugins are isolated to the block editor or SEO fields. By contrast, an AI Agent for WordPress connects directly to your site and can manage posts, media, pages, users, themes, plugins, and WooCommerce products and orders. It is an operations manager, not just a writer.
  • You need to execute the same change across hundreds of items. Manually updating prices on 300 WooCommerce products or adding missing alt text to your entire media library takes hours of clicking. An AI Agent for WordPress can make these sweeping database modifications instantly in response to a single prompt, saving you from clicking 300 times.
  • You manage multiple websites. Instead of logging into five different dashboards to perform routine updates, you can activate the AI Agent plugin on multiple WordPress installs and orchestrate actions across all of your selected domains simultaneously from a single, unified chat.
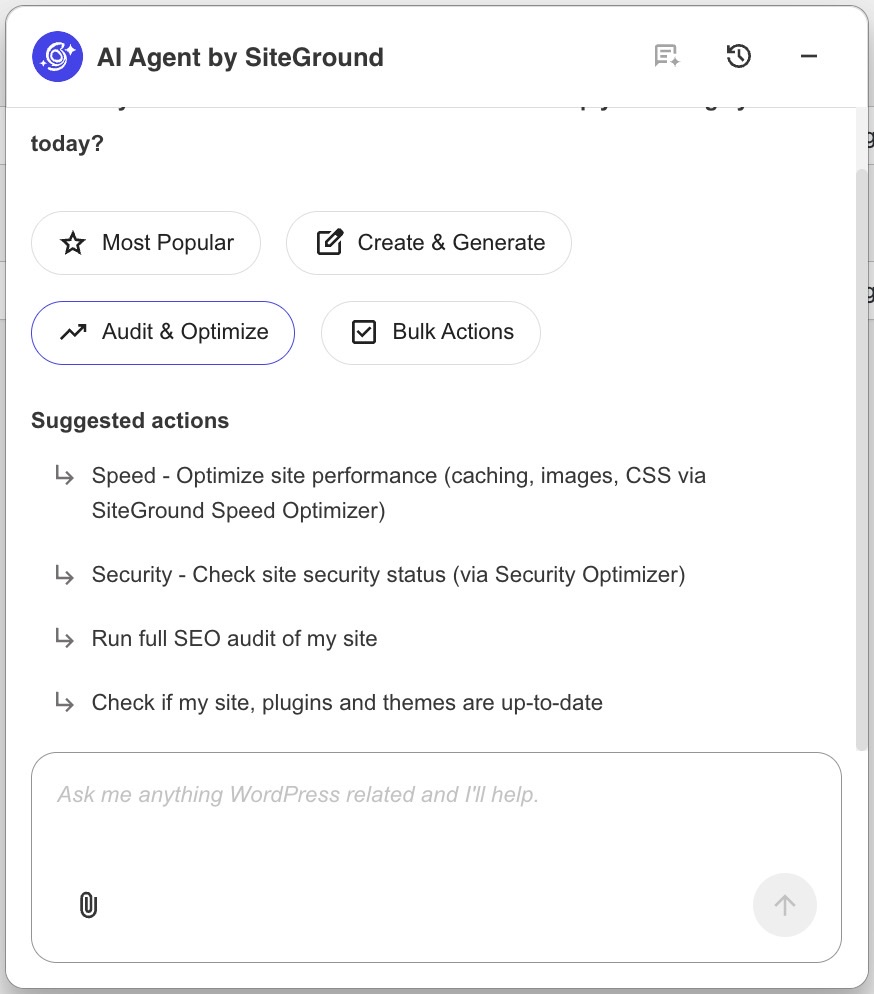
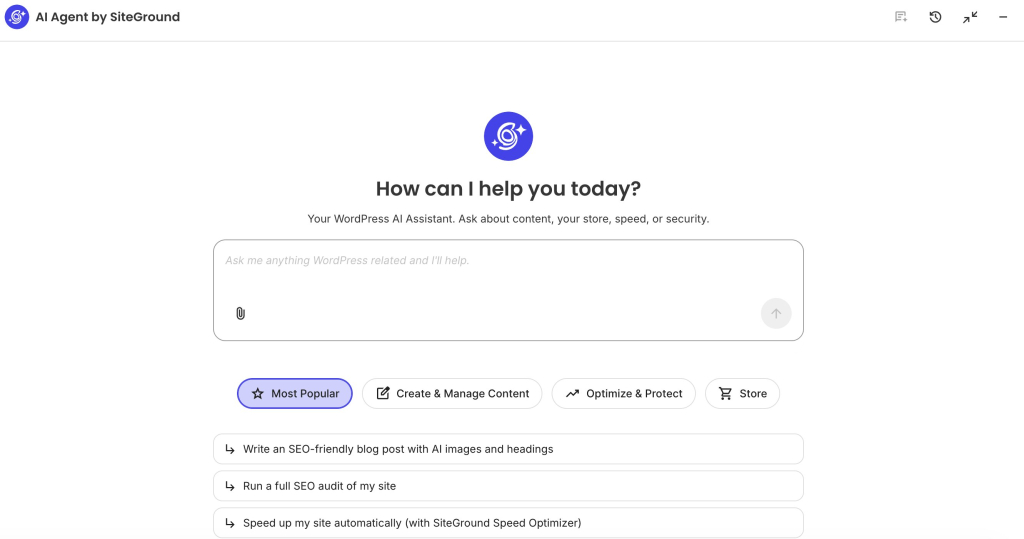
AI Agent by SiteGround chat panel with category buttons (Most Popular, Create & Generate, Audit & Optimize, Bulk Actions) and a list of suggested actions for site speed, security, SEO audit, and update checks.

What changes when you connect SiteGround AI as your WordPress AI provider 

Setting up an AI provider the standard way means a developer dashboard, a key you generate and paste in, and a bill you keep an eye on. Connecting SiteGround AI removes all three at once. There are no API keys to generate, copy, or maintain, and no separate bills from different AI providers to track. All your usage consolidates into a single AI Studio subscription, so you get one predictable monthly bill and a clear view of what you’ve used.

As your WordPress 7 AI provider, SiteGround AI powers the standard editor capabilities that any connected provider can handle. It also activates the AI Agent for WordPress, which appears as a chat box in the bottom corner of your admin dashboard. The chat is persistent, so it stays with you as you move between screens rather than being something you open, use, and close.

Behind both of those, it removes a decision most small business owners don’t have the time to make. With a provider connected directly, you’re choosing which AI model runs each request: the fast ones are cheap and shallow, the powerful ones are slower and better at hard problems.

SiteGround AI routes each request to the model that suits it. For instance, if you ask the AI Agent for WordPress for quick advice about a plugin, it goes to something light like Gemini Flash for an instant answer. Ask for something heavier, like analyzing your site database or generating secure code to update your settings, and it routes to a more powerful model such as Gemini Pro or Claude Opus. You get the right level of intelligence for each task without learning the differences between models.

WordPress 7 made your site AI-ready, not AI-managed

What all this means for you is that WordPress 7 AI features vs AI Agent for WordPress isn’t really a choice between two products. The infrastructure connects AI to your site, while an agent is what turns that connection into work getting done. One is the wiring, the other is what you plug into it. 

So the real question isn’t which one to pick, but how much of your WordPress work you want AI to help you with. 

Do WordPress 7.0 AI features include an AI assistant?

No. WordPress 7.0 ships AI infrastructure rather than AI features: the AI Client, which standardizes how WordPress communicates with AI services, and the Connectors screen, where you manage provider credentials. To get anything you can click, you install an AI plugin on top.

Can WordPress 7.0 manage plugins and WooCommerce by itself?

No. WordPress 7.0 cannot manage plugins or WooCommerce by itself. It provides the connection layer and a register of actions your site can perform, but core includes no screen or chat where you can request that work.

What is the difference between WordPress 7.0 AI and an AI agent?

The difference between WordPress 7.0 AI and an AI agent is what each one does. WordPress 7.0 connects your site to an AI provider so compatible plugins can use it. An AI agent for WordPress reads your site and acts on it, handling plugins, products, orders, and users through a chat in your admin.

Do I still need an AI agent after upgrading to WordPress 7.0?

You still need a WordPress AI management assistant such as AI Agent for WordPress after upgrading to WordPress 7.0 if you want help with site management rather than writing. The infrastructure connects AI to your site but does not provide a conversational management interface by itself, and WordPress’s own AI plugin covers the post editor only.

What do the AI Client, Connectors screen, and Abilities API each do?

The AI Client standardizes how plugins request AI work. The Connectors screen is where you connect provider accounts so plugins can share one connection. The Abilities API keeps a structured register of what your site can do, so AI tools can discover which actions are available.

Do I need separate API keys for OpenAI, Claude, and Gemini?

Yes, you need separate API keys for OpenAI, Claude, and Gemini if you connect them individually. Each provider needs its own account, its own API key entered in Settings > Connectors, and its own provider plugin activated. Connecting SiteGround AI instead registers a provider automatically, with no API key at any stage.

Is SiteGround AI Studio an AI provider or an AI agent?

Both roles come from the same plugin. SiteGround AI acts as your AI provider in Settings > Connectors, and the AI Agent for WordPress is the chat that reads and acts on your site. The AI Agent by SiteGround plugin is what connects your site to both.

What happens when AI Studio is connected to WordPress?

When AI Studio is connected to WordPress, SiteGround AI is registered automatically in Settings > Connectors and marked as connected, with no API key required. The AI Agent for WordPress becomes available as a chat across your admin, and you can switch either layer off independently.
You don’t need a developer to add Stripe to your website

A digital graphic illustrating an AI-assisted Stripe payment integration set against a blue gradient background. In the center, a product card displays a "Roaster's Choice Pack" coffee item priced at "$24.00" alongside an active "Stripe Integration" toggle switch. Overlaying the product card on the right is a dark "Payment Details" form with fields for email and credit card information above a blue "PAY $24.00" button being clicked by a cursor. In the bottom left, a prompt card shows the user query "Let customers pay on my site..." followed by an AI status reading "Updating ...".

You’ve probably heard that Stripe is one of the best ways for a small business to take payments, and whoever told you was right. But what’s less widely known is how much of it you can set up yourself: actually, you can add Stripe without a developer for most of what small businesses actually sell. 

Stripe’s no-code tools cover one-time payments, subscriptions, free trials, invoices, and donations, and they’ve absorbed a lot of what used to need custom work. What still needs building is anything that has to happen in your own system after the money arrives (and you can build it pretty easily with AI).

Key takeaways:

  • You can add Stripe without a developer for most of what small businesses sell. Products, services, deposits, donations, and memberships are all covered by tools Stripe built for people who don’t write code.
  • You can start before launching your website. A payment link is a ready-made checkout page with its own web address, which you can email, text, print as a QR code, or put on social media.
  • All of it happens in the Stripe Dashboard, which is the website you log into to run your Stripe account. It’s where you create payment links, see who paid, and change your settings. Nothing there involves code.
  • Taking the money and your own system knowing the money arrived are two separate jobs. You can use an AI builder to put the checkout inside your own site while Stripe keeps handling the transactions.

How to add Stripe without a developer: what you can do with no code

The way to add Stripe without code is to just open a Stripe account, which will give you access to the Stripe Dashboard, a website you log into the same way you’d log into your email. The account itself takes about ten minutes to open, though there are a few things to settle before you take Stripe live, including your bank details, your business information, and how your name appears on customers’ card statements.

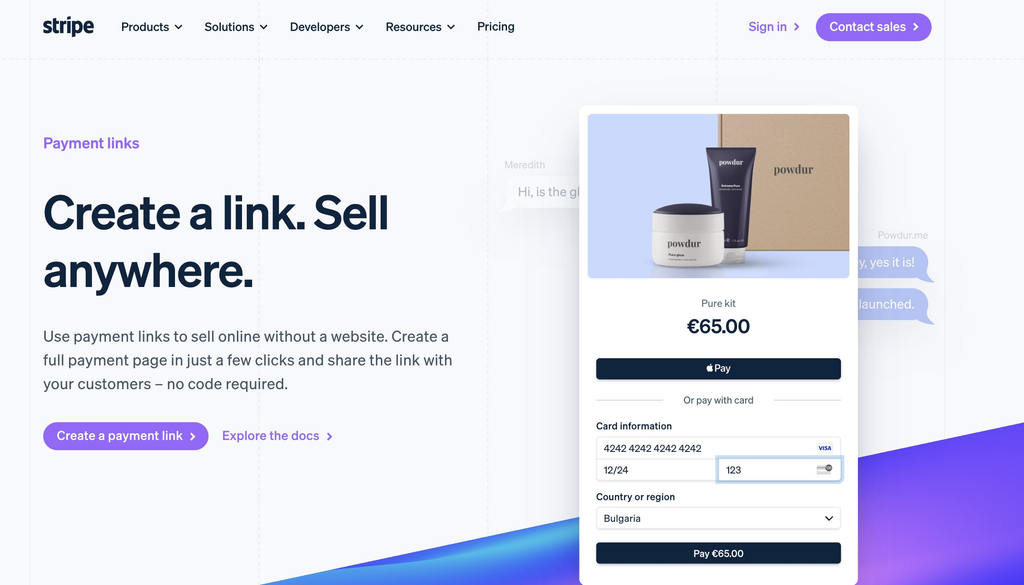
The main tool in the Stripe Dashboard is the payment link: a checkout page that Stripe builds and hosts for you, with its own web address. You create it by naming what you’re selling and what it costs, and Stripe gives you back a URL. Anyone who opens that URL sees a proper checkout page with your logo on it, pays by card or Apple Pay or Google Pay, and gets a receipt. The money lands in your bank account, and you get an email telling you it happened.

A screenshot of the Stripe landing page for Payment Links featuring the headline "Create a link. Sell anywhere." and a call-to-action button reading "Create a payment link." On the right, a floating checkout preview card displays a skincare product bundle titled "Pure kit" priced at "€65.00," featuring an Apple Pay option, credit card details entry fields, country selection dropdown set to "Bulgaria," and a dark "Pay €65.00" button against floating chat message bubbles in the background.

That’s already enough to add a payment to a website without a developer, and you can even do it before officially launching your website. You can put the link in an email to a client, send it by text, turn it into a QR code for a menu or a market stall, or post it on Instagram. If you already have a website, you can paste in a small snippet Stripe provides to turn it into a buy button on your own page.

By the way, this no-code side covers more things than you’d expect: 

What you want to doHow it works with no codeWorth knowing before you start
Sell a product or serviceCreate a payment link with a fixed price and share it, or embed it as a buy button on your siteOver 40 payment methods and 35-plus languages are handled for you, with Apple Pay and Google Pay switched on automatically
Charge monthly or yearlyCreate the same kind of link with a recurring price instead of a one-off oneStripe handles the renewals, the failed cards, and the receipts. You don’t manage any of it
Offer a free trialTurn on a trial when you create the subscription link, and choose whether to ask for a card up frontSwitch on the reminder emails as well, because Stripe pauses a trial if no card has been added by the time it ends
Bill a client for agreed workSend a Stripe invoice, which is a hosted page they can pay and download for their recordsUsually a better fit than a payment link when the amount changes from job to job
Take tips or donationsCreate a link where the customer chooses the amountThere’s a default ceiling of 10,000 USD per payment, and this option doesn’t work for recurring gifts
Show your prices on your siteBuild a pricing table in the Dashboard and paste the snippet onto your pagePairs well with payment links for memberships, courses, or software
Add extras at checkoutTurn on optional add-on items, discount codes, and shipping rates when you create the linkAll of it is configured with dropdowns and text fields
Limit how many people can buySet a cap on how many times a link can be paid, after which it stops workingUseful for event tickets, limited stock, or a launch offer

Complex operations like recurring billing (charging monthly or yearly) sound like the point where you’d need help, because someone has to charge the card every month or stop charging when people cancel, but Stripe takes care of all of that. You just set a price and a frequency, share the link, and it runs. This way, you can easily build a subscription business in an afternoon.

Free trials go one step further: you can let someone start a trial without giving you a card at all, which removes the biggest reason people abandon a signup. The catch is small and worth setting up at the same time: unless you switch on the emails that prompt them to add a card before the trial ends, Stripe pauses the subscription rather than charging them. Turn those on when you create the link, and it takes care of itself.

Pro tip: Make your first payment link before you decide anything else. It costs nothing, takes about five minutes, and it’s the fastest way to find out whether you need anything more. Create one for the thing you sell most often and send it to yourself. You’ll see exactly what your customer sees, what the receipt looks like, and what lands in your inbox when it’s paid. Plenty of people discover at that point that the job is already done, and the ones who don’t now know precisely which part is missing, which is a much better position to be in than guessing.

Where the no-code path runs out

Stripe’s no-code tools have their limitations, which might affect you depending on what you sell and how you deliver it:

The limitWhat it means for youWhen it becomes a problem
Your website learns nothingStripe emails you and shows the payment in your Dashboard. It doesn’t tell your site, your database, or your member areaWhen paying is supposed to grant access, confirm a booking, or start something automatically
Limited design controlYou can add your logo, pick your background and button colors, and choose from a set of preset fonts. You can’t change the layoutWhen you’ve paid for a designed site and the checkout page looks like a different company
Customers leave your site to payClicking your buy button takes them to a Stripe page, then brings them back afterwardRarely, in practice. Most people recognize Stripe and trust it. It bothers some brands more than their customers
Everything has to be a fixed productPayment links are built around items with set prices, so variable amounts mean creating a lot of links or asking customers to type a numberWhen you quote every job differently, which is most consultants, trades, and agencies
Caps on pay-what-you-wantA default maximum of 10,000 USD per payment, and no support for recurring amountsLarge deposits, retainers, and donation programs. The cap can be raised by asking Stripe
No rules of your ownAnything conditional, like different pricing for different customers or a follow-up that happens automaticallyThis is the genuine dividing line between configuring and building

The first limitation is probably the most significant one: Stripe has no connection to whatever you’ve built, so it can’t log a customer into a members area, mark an order as paid in your booking system, add someone to a course, or update a record in the spreadsheet you run your business on. 

For a lot of small businesses, that’s completely fine. If you take a deposit and then phone the customer to arrange the work, nothing needed to happen automatically. If you sell a physical product and pack it yourself, an email telling you to pack it is all you need. The gap only becomes a problem when the payment is supposed to update a record in an app you already built.

When do you need a developer for Stripe?

Picture someone paying you, and ask what needs to happen the moment the payment goes through. If the answer is that you find out and the money reaches your bank, you’re good to go. You can build the whole thing yourself this afternoon. If the answer involves something else happening, without you doing it, keep reading.

You don’t need a developer if Stripe’s tools are enough

You can accept Stripe payments without a developer if you’re selling a set number of things at set prices, taking deposits or donations, running a subscription, or invoicing clients for work you’ve agreed to. You also need to be comfortable with customers paying on Stripe Checkout, which is the hosted page they get sent to. For most small businesses, that’s a non-issue and occasionally an advantage, since people recognize the name.

That covers a lot of real businesses. A consultant selling three service packages, a restaurant taking deposits, a gym running memberships, a charity collecting donations or even a full ecommerce platform all sit comfortably inside the no-code surface. 

You might need a developer if you want more than the Stripe Dashboard

You’ve outgrown Stripe’s no-code options when paying has to give someone access to something you’ve built, when the checkout needs to sit on your own page with your own design, when the amount is worked out rather than picked from a list, or when something has to happen by itself once the money arrives.

A membership site is a good example: someone pays, and they should be able to log in and see the content immediately. Stripe can take that payment perfectly well, but it has no way to create their account or let them in. 

However, custom payment builds can get expensive. That’s why you should also know that needing more than the Stripe Dashboard and needing to hire a developer aren’t the same thing. There’s a route in between.

The middle path: add Stripe to your own site or app without custom code

What if you can get the checkout on your own site, styled like the rest of it, connected to whatever should happen next, and you still don’t write any code? 

An AI builder for launching without developers can do exactly this by building the connection for you. You describe the payment behavior you want, and it builds the checkout into your site and connects your own Stripe account, with the card handling still happening on Stripe’s side. Because the flow lives in your app, it can also do what payment links can’t: update a record, grant access, or mark an order paid when the payment succeeds. 

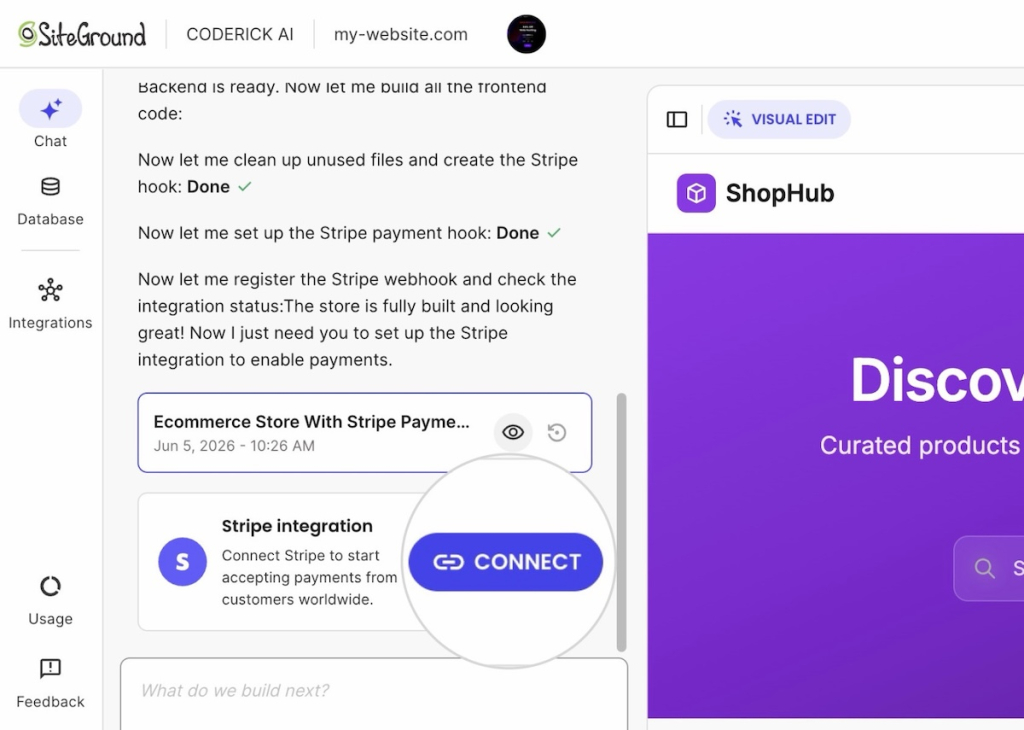
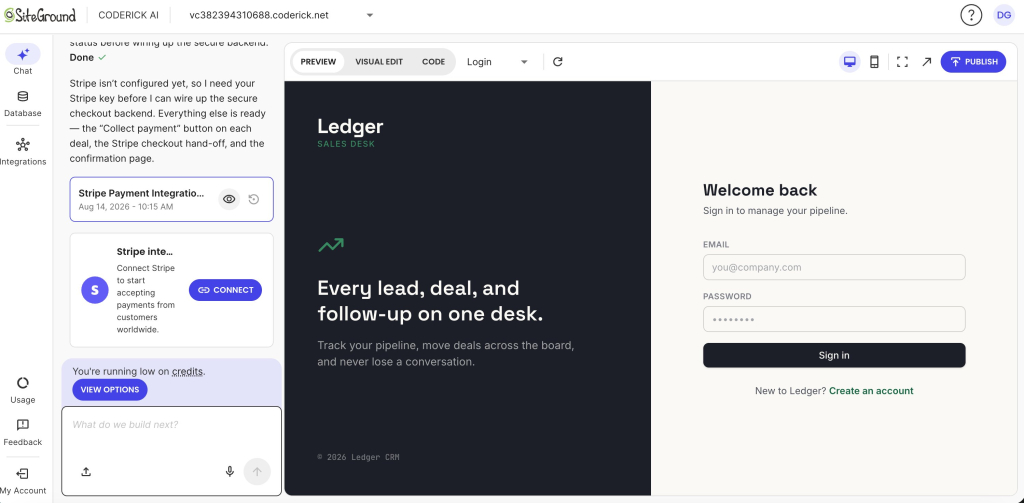
If you use an advanced AI builder like Coderick AI, it will read the payment intent in your prompts and will show a Stripe connection card inside the chat interface:

Example of connecting Stripe payments to a client's AI built website

From there it’s a few clicks and one paste. You click Connect, and Coderick AI asks for a key from your Stripe account.

Stripe issues what it calls a Restricted Key, which starts with rk_, and it isn’t your account password. It can only do the specific things Coderick AI needs, and you can change its permissions or switch it off from your Stripe Dashboard whenever you want. 

Once the key validates, the card flips to Connected and Coderick sets up the rest in the background: your product list, and the connection that listens for payments. When someone buys, Stripe confirms the payment back to your site and your order records update to paid without anyone touching them.

Read our guide to setting up Stripe inside Coderick AI to learn about the full process (which takes about a minute). 

What to check before you take real payments

Whichever route you take with Stripe, spend twenty minutes on these four checks before a real customer pays you.

  • Pay yourself in test mode. Stripe gives every account a test mode, which is a complete copy of the system where nothing is real. You can put a fake card through your own checkout and watch the whole thing work without any money moving. Switch it on, buy your own product, and see what happens.
  • Try a card that fails. Stripe publishes test card numbers that are designed to be declined. Use one and check that nothing gets marked as paid, and that the customer sees something sensible rather than a blank page.
  • Find out where the notification goes. Know which inbox receives the payment email and who actually reads it. A payment nobody notices for three days is a fulfillment problem, and it’s the most common one.
  • Look at what the customer sees afterward. The confirmation page and the receipt are part of what they’re buying, and both can be edited. Check that they say something you’d be happy to receive.

Pro tip: Run the same test on your phone. You’ll do the four checks above on whatever you built the site on, which is almost certainly a desktop. Most of your customers won’t be. Checkout is the part of a site most likely to behave differently on a small screen, and it’s the part where a problem costs you the sale rather than a page view. Repeat your test order on a phone before you do anything else. And if you’ve built the store around that checkout with AI, there are eight things worth verifying before real money moves.

Stripe without a developer: the 10-minute test

Whether you can add Stripe without a developer has almost nothing to do with how technical you are. It comes down to one thing: whether anything has to happen after the payment. If the money arrives and an email telling you about it is the whole job, you can have this working before the end of the day, for free, using tools Stripe built for exactly this.

If something on your own site does have to change when someone pays, that’s a genuinely different piece of work. It’s still not a reason to hire a developer, because the gap between a Stripe-hosted link and a custom build is now filled by AI builders that do the connecting for you.

So answer the question before you spend anything on custom development. Open Stripe, make a payment link for the thing you sell, and send it to yourself. Ten minutes later you’ll know whether you’re finished or whether you need the middle path, and either answer saves you a quote you didn’t need.

[96]

FAQs

Do I need a developer to add Stripe to my website?

You don’t need a developer to add Stripe to your website for most common cases. Stripe’s no-code tools handle one-time payments, subscriptions, free trials, invoices, and donations. You need help when a payment has to change something in your own system, when the checkout must sit on your own branded page, or when amounts and rules are custom.

Can I add Stripe to my website without hiring a developer?

Yes. You can add Stripe to your website without hiring a developer by creating a payment link in the Stripe Dashboard and pasting Stripe’s snippet onto your page as a buy button. You can also skip the website entirely and share the link by email, text, or QR code.

Can I use Stripe without writing code?

Yes. You can use Stripe without writing code through payment links, invoices, quotes, pricing tables, and subscriptions, all created in the Stripe Dashboard. Stripe notifies you when someone pays and deposits the money in your bank account, so no code is needed for the payment itself.

What is the easiest way to add Stripe payments to a website?

The easiest way to add Stripe payments to a website is to create a payment link in the Stripe Dashboard and embed it as a buy button. It takes about five minutes, costs nothing to set up, and requires no code.

What Stripe payment flows can I launch without custom code?

Without custom code you can launch one-time product sales, monthly or yearly subscriptions, free trials that start without card details, tips, donations, pay-what-you-want payments up to a default cap, invoices, quotes, and a pricing table on your own site.

Can I accept subscriptions without a Stripe developer?

Yes. You can accept subscriptions without a Stripe developer by creating a payment link with a recurring price. Stripe handles renewals, failed cards, and receipts. You can also offer a free trial without asking for a card, as long as you switch on the reminder emails that prompt customers before the trial ends.

Can I accept one-time payments without a Stripe developer?

Yes. You can accept one-time payments without a Stripe developer using a payment link, an invoice, or a buy button on your own page. All three are created in the Stripe Dashboard and need no code.

Can I build a payment-ready website without a developer?

Yes. You can build a payment-ready website without a developer by using an AI builder to create the site and the checkout together, connected to your own Stripe account. Stripe still handles the card details, and because the checkout lives in your site, the payment can also update your own records.

Payment gateway fees and costs: what small businesses should expect

Abstract image of payment gateway fees

At first blush, payment gateway fees seem pretty straightforward: a processor takes a small cut of every transaction, and that’s the end of it. But when all is said and done, that also means getting checkout live, keeping it running, covering the fees that only show up when something goes sideways, and cleaning up after any mistakes that show up three months in. Knowing these costs beforehand turns a surprise bill into a number you already expected.

Key takeaways:

  • Payment gateway fees typically run around 2.9% plus $0.30 per online card transaction in the US, but that line is rarely the full bill.
  • Checkout setup cost ranges from minutes to connect payments through an existing platform to several weeks for a custom developer build.
  • Whether checkout, inventory, and order records stay connected automatically or need manual wiring by hand depends entirely on which setup approach is used.
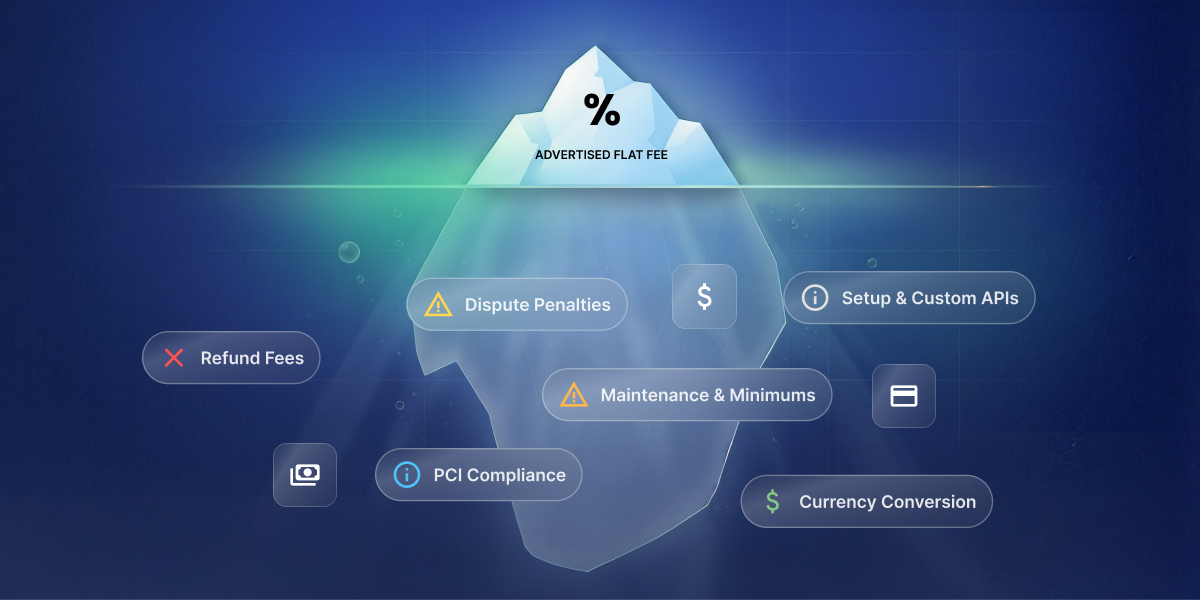
  • Hidden payment gateway fees, including refund fees, dispute fees, currency conversion, PCI compliance charges, and platform-level transaction fees, add up fast when nobody’s tracking them.
  • A payment dispute typically triggers a $15 flat fee on top of the disputed amount, refunded by some processors on a win, kept by most on a loss.
  • Subscription businesses carry extra payment costs beyond one-time sellers: failed-renewal churn, plus often a separate billing-tool fee on top of standard processing.
  • Disconnected tools, a payment processor that doesn’t talk to your accounting software or CRM, cost more in reconciliation time than in fees.

What are payment gateway fees, really?

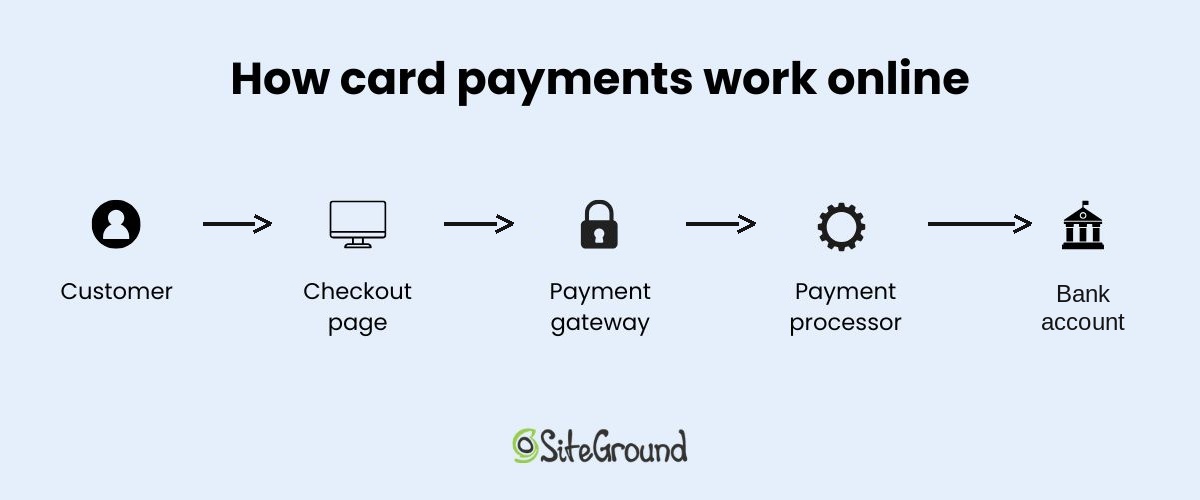
Payment gateway fees are the cut a payment processor keeps for handling a card transaction, usually a percentage of the sale, plus a small flat fee. Here’s what that looks like on a single transaction:

  1. A gateway captures the customer’s card details at checkout.
  2. A processor moves the money and takes its cut. For example, Stripe fees are 2.9% plus $0.30 per successful US card charge, with no monthly fee on its Standard plan.
  3. The payout lands in the business’s bank account a few days later, minus that fee.
A diagram showing the flow of how payments work online, from the customer to checkout, payment gateway, payment processor, and bank account

That fee, though, is the smallest number when it comes to how businesses accept payments online, and the one most comparison articles stop at. It doesn’t cover what it takes to get checkout live or keep it running, which is where the real budget lives.

Note: All fees and plan details in this article are as of August 2026. Stripe’s the running example throughout this piece because its pricing is public and it’s a common default for small businesses; PayPal, Square, and other major processors land in a similar range, just with their own rate cards, so the cost categories below apply no matter which one ends up running checkout. Getting these Stripe basics down early makes the rest of this easier to follow.

What it costs to get payments live

Indeed, most people underestimate the total cost of taking payments. They see the processor’s fee and stop there, and yet, in practice, there’s a lot more to actually getting paid. Part of that is dictated by your setup approach, which determines how much time you’ll be spending getting everything live. 

What kind of setup complexity are you looking at? It comes down to who builds the payment experience and where it lives. That splits into five basic setups:

  1. DIY with Stripe’s API (Stripe Elements): you write the code yourself, and the payment form lives directly on your own site. Best suited to a business owner comfortable coding a fairly simple checkout personally, using Stripe’s own building blocks rather than hiring anyone.
  2. Stripe Checkout: Stripe hands over a pre-built, hosted page; customers get redirected there and back.
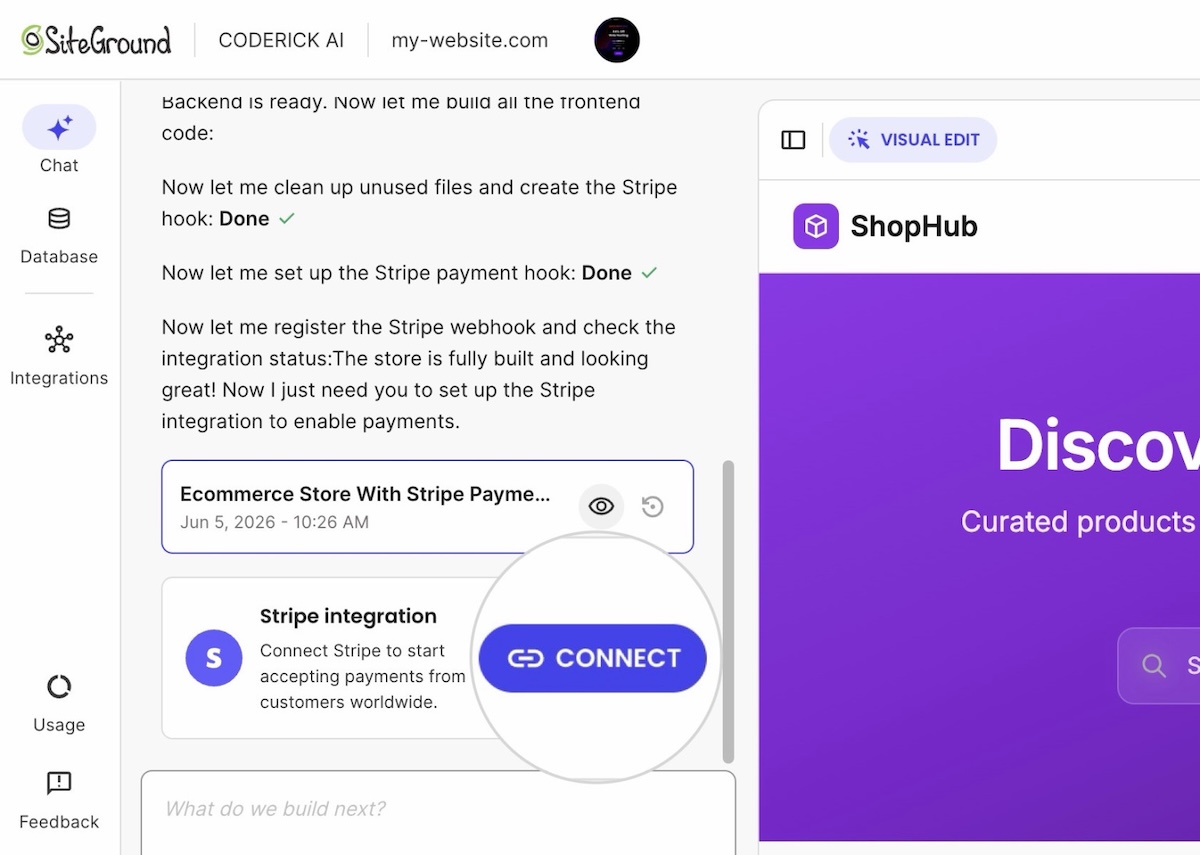
  3. Coderick AI (SiteGround’s AI website and app builder): describing the store to it is the entire setup step, no custom Stripe build required. The store, products, and checkout flow live inside your site’s own design; the payment window itself, where the card gets entered, is Stripe’s. No page to design, no API to wire up. The screenshot below shows this step in action: Coderick AI registering Stripe’s own confirmation webhook, the internal signal that tells the app a payment succeeded, not a connection to any outside tool.
Example of connecting Stripe payments to a client's AI built website
  1. Custom development: a hired developer builds it, anything from a simple embedded form to a multi-step, split-payment checkout. Unlike DIY, someone else does the coding, which removes the ceiling DIY has on complexity, at the cost of paying for that work instead of spending your own time.
  2. A full ecommerce platform, such as SiteGround Ecommerce: signing up for the platform is the setup step. Checkout lives inside the platform’s own storefront, with Stripe (or an equivalent) running underneath.

That last one is a bigger decision than the other four: it comes with a storefront and product catalog attached, not just a way to take payments. That bigger footprint earns its keep for a catalog-driven store that needs shipping, tax, and marketing tooling built in from day one. For a handful of products or a single checkout flow, it’s often more machinery than the job needs, and Coderick AI or Stripe Checkout gets there faster.

Time and cost still swing widely across all five, though. Here’s the breakdown:

Checkout setup cost

ApproachSetup timeSetup costTypically used for
DIY with Stripe’s APIA few hours to a few days$0 in tool fees, unpaid time spent building itDevelopers writing their own integration by hand
Stripe CheckoutA few hours$0 setup fee, standard processing rateA fast payment page that doesn’t touch the site’s design
Coderick AISame day$10 to $40 a month, no developer invoiceGetting a store live the same day without writing or hiring for code
Custom developmentTwo to six-plus weeks$5,000 to $50,000-plus upfront, then hourly for changesComplex logic: marketplaces, split payments, unusual rules
Full ecommerce platformA few minutes to a few hours to connect payments$18 to $36 a month, no separate developer cost A full storefront and checkout bundled into one signup

That table covers building a checkout, five ways to do it. For anyone comparing a lighter ecommerce setup against building everything from scratch, the fifth row is the one to study most closely. Turning any of these into a working checkout that can actually run a business adds to the payment integration cost, regardless of approach.

What payment integration cost actually includes

Moving the money is the easy part. A working checkout also needs:

  • Order confirmation emails: a basic payment receipt often comes free once that setting’s turned on, but a proper order confirmation with your own branding and order details is usually separate logic that needs building or wiring up.
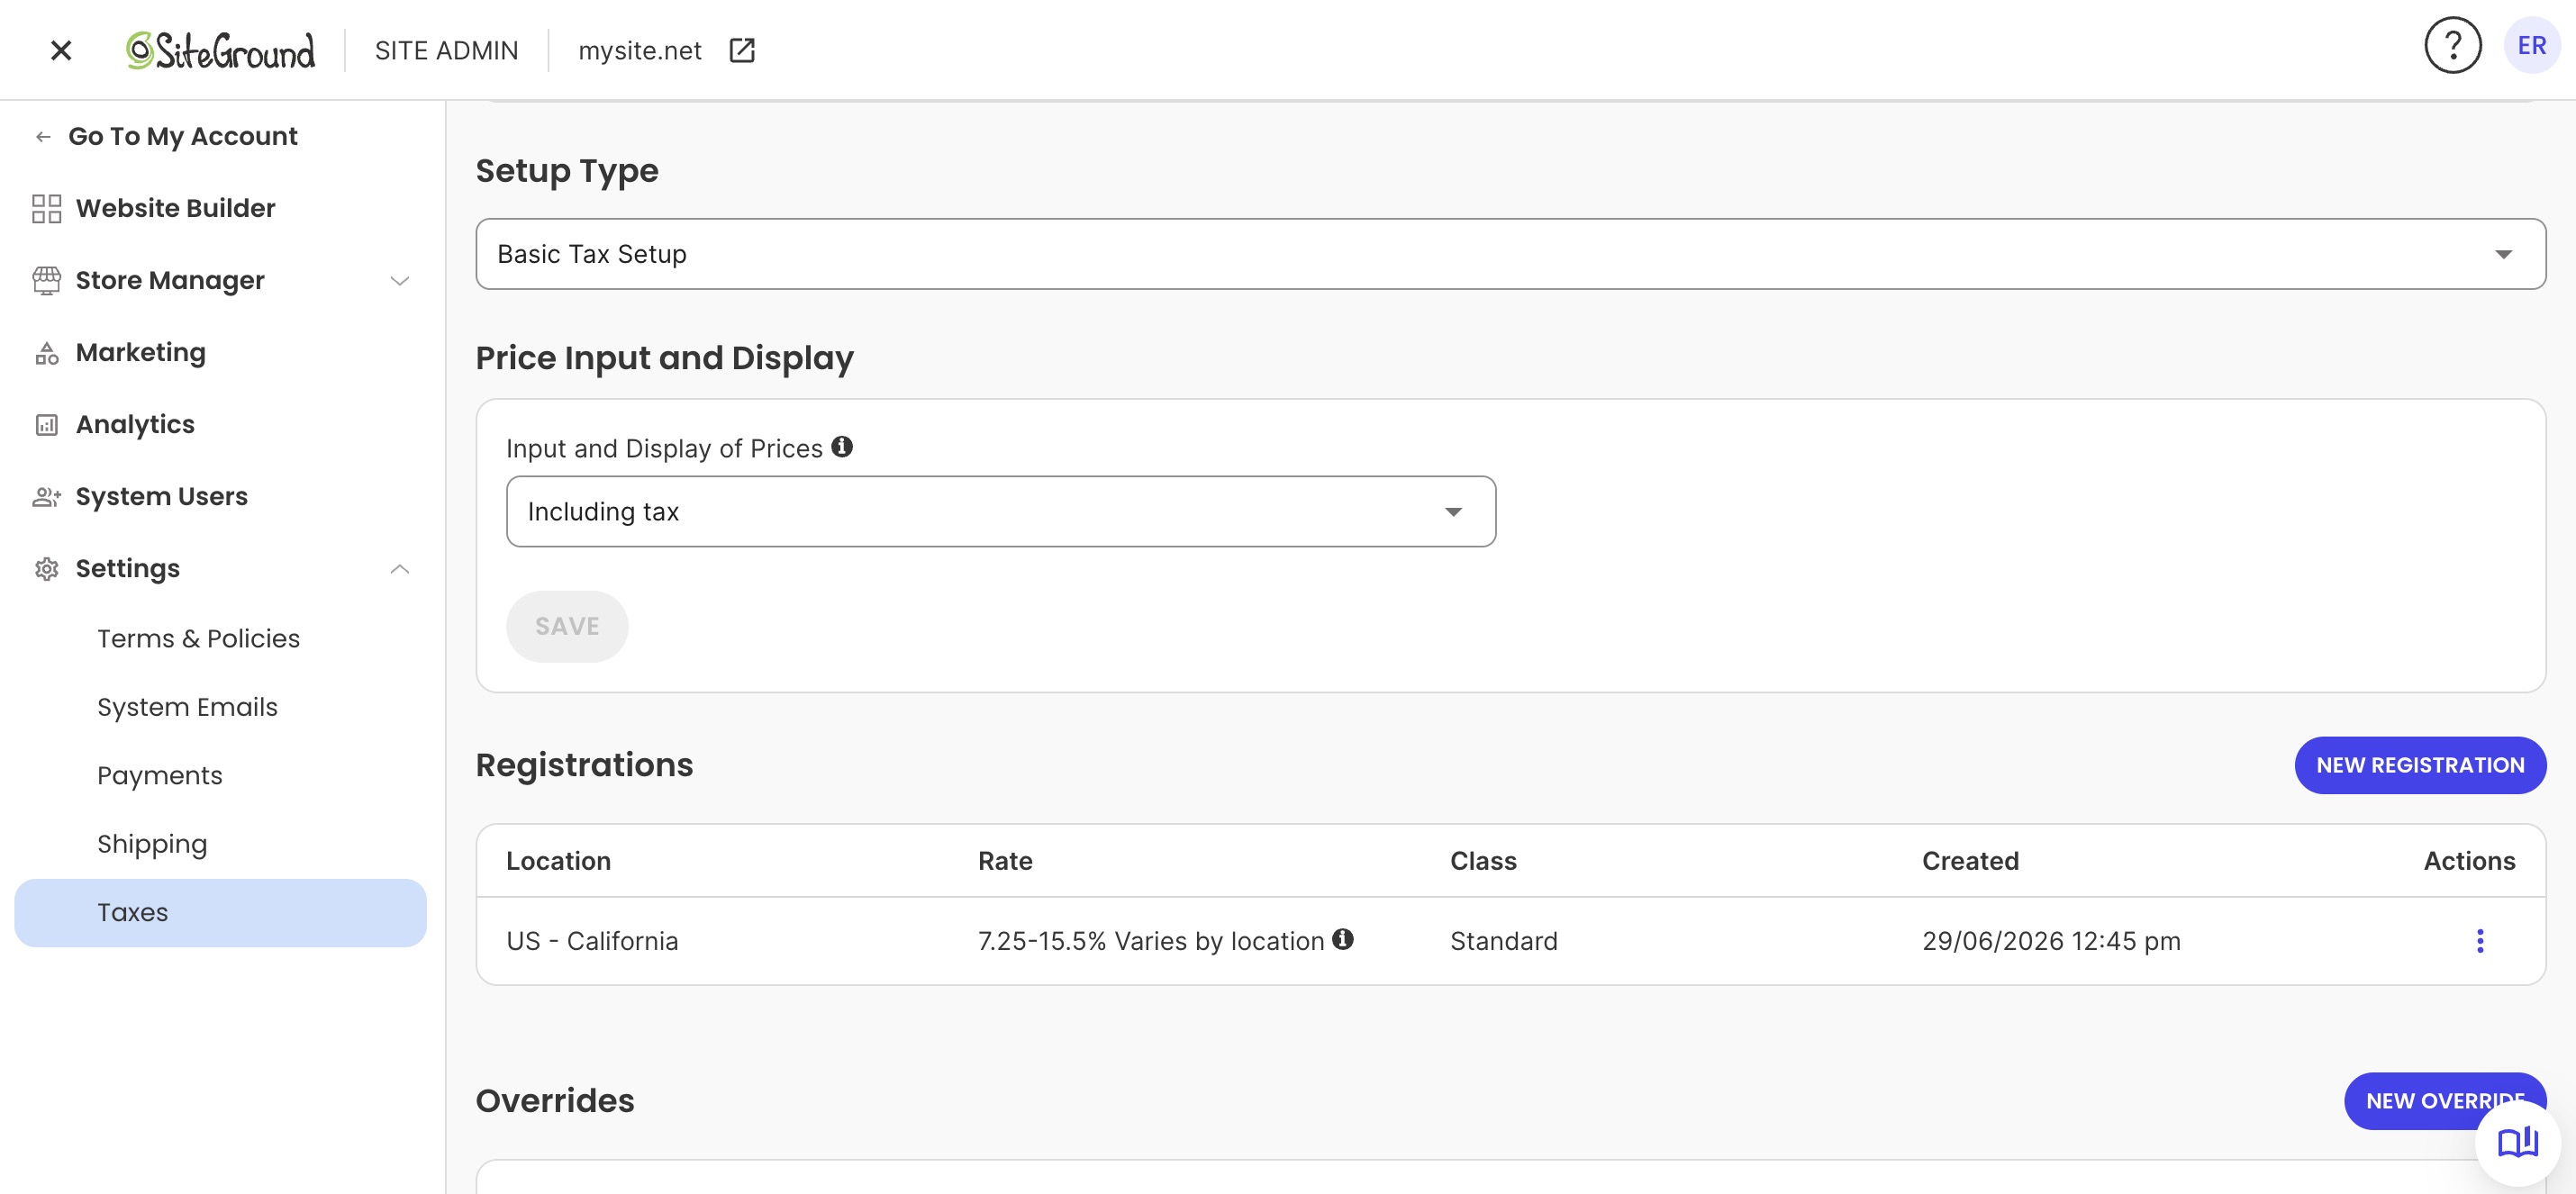
  • Tax calculation: applying the right ecommerce sales tax based on where the customer’s buying from. Stripe Tax is available with its own fee whether Stripe runs directly or through an ecommerce platform’s tax settings (as seen below); otherwise it’s a dedicated tax service or manual handling.
Choosing configuration of the Basic Tax Setup with SiteGround Ecommerce
  • Inventory updates: no payment processor tracks what’s in stock, that’s a store feature, not a payment one.
  • Refund handling your team can use without needing direct access to the processor’s own dashboard: most processors already have a one-click refund button built in, so this only becomes a build item if refunds need to happen from your own admin panel or CRM instead, and even then, the processor’s own API key needs refund permissions specifically enabled for it to actually work.

Who this applies to: DIY, Stripe Checkout, and custom development mean connecting these pieces (confirmations, tax, inventory, refunds) by hand, self-taught code or a developer’s invoice. A full ecommerce platform ships with them already built in; Coderick AI can build the same pieces if specifically asked, but that takes prompting and testing, not something that comes bundled by default.

None of this applies to a single one-off payment, a portfolio deposit, a restaurant reservation hold, an event ticket, as a hosted payment link or an embedded pay button covers these simple payment flows instead. An ongoing store needs all of it. 

Payment maintenance costs after launch

Payment maintenance costs don’t show up on the invoice for getting checkout live. They only start once a checkout’s actually been running for a while, and they come in two flavors: keeping tools connected to each other, and handling renewal payments that don’t go through cleanly if the plan includes subscriptions. Let’s break it down.

How disconnected tools add to your maintenance costs

Watch for this pattern: checkout runs through one tool, bookkeeping happens in a separate accounting app, and payment status in your CRM or project tool sits disconnected from both. Disconnected integrations like this turn every sale into:

  • Copying the transaction into the books by hand
  • Updating the order or client record separately
  • Matching any refund across all three, so nothing gets missed

For agencies invoicing multiple clients, closing this exact gap, checkout status not showing up where the client record lives, is usually the difference between faster client payments and constantly chasing down who’s actually paid.

Who this applies to: all five setups. Custom development can have an accounting or CRM connection built in, for a price. The other four handle payment confirmation internally, that’s how any checkout works at all, but none of them expose a way to connect out to a separate accounting or CRM tool.

The fix: a manual routine, though what that actually looks like depends on the setup:

  • Full ecommerce platform: often handled through a built-in order export.
  • Coderick AI: doesn’t include one by default, but it can be asked to add an export option, and refined further with more specific instructions if needed. It still can’t create a live connection to an external accounting or CRM tool.
  • DIY and Stripe Checkout: writing that export step yourself.
  • No export at all: block off ten minutes a week to copy new orders and refunds into the books and the client tracker by hand.

Recurring payment costs for subscription businesses

Anyone building a subscription business should budget for involuntary churn from the start. Imagine: a card expires or a bank declines a renewal, the subscription lapses unless something catches it, and sales go down. Two things reduce this:

  • Automatic retries: re-attempting a failed renewal a few times over one to two weeks, sometimes on by default, sometimes a setting to turn on
  • Card-expiration emails: sent before the renewal date instead of only after it fails, though this is often a setting that needs switching on rather than something that happens automatically

Who this applies to: it depends on whether a subscription layer already sits on top of the processor. A full ecommerce platform or a dedicated subscription app usually handles both without the business owner touching a setting; wiring a processor directly means checking what’s on by default and switching on the rest.

There’s a second cost to plan for on top of that: processors that offer dedicated subscription tools, automated invoicing, retries, dunning, usage tracking, often charge extra for it. For example, Stripe’s version, Stripe Billing, adds a flat 0.7% of subscription volume on top of its standard 2.9% plus $0.30 per charge. Treat both the churn risk and this extra billing fee as built-in costs of running subscriptions at all, not one-off surprises to troubleshoot later.

The hidden costs behind payment gateway fees

Maintenance costs show up on a predictable timeline, whether or not anything goes wrong. Hidden payment gateway fees are different: they only show up when something other than a clean, successful sale happens. Refunds, disputes, and a handful of smaller charges all live here.

  • Refund fees: most processors don’t charge extra to process a refund, but they typically don’t return the original processing fee either. Refund a $50 sale, and the $1.75 already paid to accept it (2.9% plus $0.30) is usually gone for good.
  • Dispute fees: a chargeback usually triggers a separate $15 flat fee on top of the disputed amount, refunded by some processors if the merchant wins, kept by most if they lose.
  • Currency conversion and cross-border fees: expect another percentage point or two on top of the standard rate whenever a customer pays in a different currency or from a different country.
  • Monthly minimums and PCI compliance fees: PCI compliance is the security standard card networks require for handling card data safely, usually confirmed through a short questionnaire. Modern processors like Stripe handle most of this through their own checkout tools, so it rarely shows up as a separate charge. Traditional merchant account providers are a different story: some still charge a monthly non-compliance fee, often $20 to $100, for skipping the paperwork.

Platform fees stacked on top of processing fees

Some ecommerce platforms and website builders add their own per-transaction cut on top of whatever the payment processor already charges. That’s a second fee stacked on every sale, not a replacement for the first, and it’s easy to miss when comparing platforms by their processing rate alone.

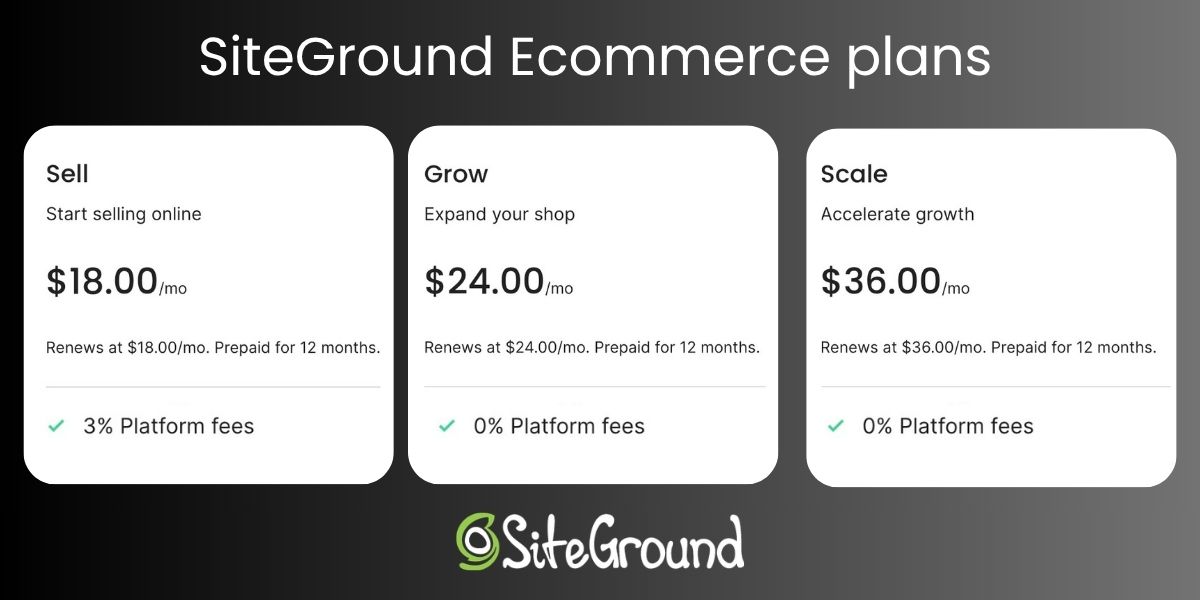
Who this applies to: the ecommerce platform route specifically. DIY, Stripe Checkout, custom development, and Coderick AI don’t have a platform layer sitting between the processor and the sale, so there’s no platform fee. SiteGround Ecommerce, for example, drops that extra fee entirely on its Grow and Scale plans, leaving just standard processing, a detail that matters when comparing platforms for selling digital or physical products. Sell runs $18 a month plus the 3% fee, Grow is $24 with none, so past roughly $200 in monthly sales, upgrading pays for itself.

The three different SiteGround Ecommerce plans - Sell, Grow and Scale

Common payment setup mistakes that cost you more later

Every cost covered so far is baked into how payments work, no mistake required. What follows is different: these are payment launch risks, avoidable and rare on launch day itself. They show up the first time something other than a clean transaction happens: the first refund, the first disputed charge, the first server change. 

1. Never testing a real transaction end to end

A checkout that “looks” done and a checkout that’s actually processed a real card, a refund, and a confirmation email are different things. Test all three before launch, including what a customer sees when a card gets declined.

Who this applies to: every setup, regardless of path.

2. Moving hosting without re-checking payment notifications

A site migration is a common place for this exact mistake to surface: moving a live site to new hosting can leave the automatic message a processor sends to confirm a payment pointed at a server that no longer exists, so an order shows “confirmed” on the site while the payment never actually clears on the backend. That kind of gap can run for a couple of days before a customer emails to ask where their order is.

Who this applies to: self-managed hosting, DIY or custom development. A managed platform like Coderick AI or a full ecommerce platform includes hosting already set up for the merchant, so there’s no server to move or a payment notification to break in the first place.

3. Leaving test API keys live in production

Real charges silently fail, or a store looks like it’s taking payments when it’s actually just running in test mode, when test and live keys get mixed up.

Who this applies to: DIY and custom development, where a live key can end up hardcoded into exposed project files. Coderick AI has a dedicated popup for pasting in a Stripe restricted key, separate from typing it into the chat or the project’s code directly. It’s still worth confirming it’s the right key, test or live, each time.

4. Treating PCI compliance as optional

It isn’t a suggestion. For Stripe-based setups, skipping it usually doesn’t show up as its own line item, since Stripe absorbs most of the compliance work into its own tools, but it still raises liability if a breach happens.

Who this applies to: everyone, though the consequence differs by setup. For example, when it comes to Coderick AI, customers enter their card details directly through Stripe, so Coderick AI itself never handles the card data, and there’s no PCI compliance for Coderick AI to carry in the first place. On a traditional merchant account, it’s more direct: skipping it is how a monthly non-compliance fee ends up on a statement.

So, what do payment gateway fees really cost?

Here’s what all of this can look like in practice for a small store doing around $5,000 a month in sales, 100 orders averaging $50 each:

CostAmountThe math
Processing fees$1752.9% + $0.30 per order, across 100 orders
Platform fee (Sell tier)$1503% of $5,000 in monthly sales
One dispute$15Flat fee per chargeback
Total$340

That’s before the one-time cost of getting checkout live in the first place, or the cost of fixing a mistake made at launch. 

Payment gateway fees, and what comes next

Payment gateway fees are the smallest, most visible line in this whole picture. The real total is provider fees plus setup time plus ongoing maintenance plus whatever a rushed launch costs to fix later, and that last category is the one most small businesses pay for without ever seeing it itemized. Which of these apply, and how much, depends entirely on the path in question.

Coderick AI’s distinct advantage in this comparison is the build process itself: whatever gets described (checkout, inventory tracking, order records) comes out connected, and updates work the same way, describing a change instead of filing one with a developer. That’s what makes it the right fit for a single checkout or a lean store built around exactly what’s needed. Build with Coderick AI to get the same connected checkout without paying a developer to build it.

[96]

Frequently asked questions

What are payment gateway fees?

Payment gateway fees are what a payment processor charges to move money from a customer’s card to a business’s bank account, typically a percentage of the sale plus a small fixed amount per transaction.

What do payment gateway fees include beyond transaction fees?

Payment gateway fees themselves usually cover just the per-transaction rate. The broader payment gateway costs around them, refund handling, dispute fees, currency conversion, and monthly minimums, gets billed separately and often gets missed when comparing providers.

What hidden payment gateway fees should small businesses know about?

Hidden payment gateway fees include refund fees (the processing fee that doesn’t come back on a refund), dispute fees, cross-border and currency conversion charges, and PCI compliance fees for skipping the annual security questionnaire.

How much does it really cost a small business to take payments online?

The real cost of taking payments online is the processing rate plus setup time plus ongoing maintenance plus the cost of fixing launch mistakes, not just the percentage listed on a pricing page. The processing rate alone is usually the smallest piece of that total.

What does checkout setup cost for a website?

Checkout setup cost for a website ranges from minutes to connect payments through an existing platform to several weeks and several thousand dollars with a custom developer build.

What does payment integration cost for a small business?

Payment integration cost for a small business covers more than connecting a processor: order confirmation emails, tax calculation, inventory syncing, and refund handling all need building or configuring too.

What payment maintenance costs continue after launch?

Payment maintenance costs after launch include handling failed or expired cards, retrying subscription renewals, and keeping payment records synced with accounting or CRM tools.

What payment setup mistakes make online payments more expensive?

Payment setup mistakes that make online payments more expensive include skipping end-to-end testing, missing a payment notification update after a hosting migration, mixing up test and live API keys, and treating PCI compliance as optional.

Do refund fees and dispute fees increase payment costs?

Yes. Refund fees and dispute fees increase payment costs because most processors keep the original processing fee on a refund and charge a separate flat fee for every dispute, refunded by some processors on a win, kept by most on a loss.

Is Stripe Checkout cheaper than building a custom checkout?

Stripe Checkout is usually cheaper than building a custom checkout, since it skips developer hours entirely, though Stripe checkout in Coderick AI can be faster still because it handles the surrounding integration work, such as order records and confirmation emails, too.

Web app ideas for beginners: 10 AI projects to start this weekend

Header image of a hand holding a smartphone with a web app dashboard and floating Planner, Quote Planner, and No Code labels.

The hardest part of a first web app isn’t the building. It’s picking something small enough to finish. Most web app ideas lists hand you a marketplace, call it a weekend project, and move on. These 10 web app ideas for beginners are genuinely weekend-sized: one job each, no payments, no integrations, and a copy-ready prompt to start from.

A simple beginner web app is a single-purpose tool that collects, organizes, or calculates one kind of information for a small group of people. It has one main screen, one type of data, and no dependency on outside accounts or services. Think guest list, packing planner, or quote calculator instead of platform.

Key takeaways:

  • The 10 simple web app ideas below share the same shape: one screen, one data type, and zero third-party integrations, which is what keeps a first build inside two days instead of two months.
  • A first version should hold about 5 fields and 1 view. Anything you add beyond that roughly doubles the number of things that can break before you finish.
  • Payments, user accounts, notifications, and file uploads are the four features that turn a weekend project into a month-long project. Leave all four out of version 1.
  • Every idea here works with data you already have on your phone or in a spreadsheet, so you can test with 20 real entries the same day you build.
  • Each idea includes a success check that takes under 5 minutes, because an app that looks finished and an app that works are different things.
  • Coderick AI comes with a SiteGround hosting plan rather than a separate subscription, and every plan includes at least one project slot, which is all a first build needs.

What makes a simple web app idea small enough for a weekend

A weekend-sized app stores one kind of thing and answers one question about it. A guest-list tracker stores guests and answers “how many people are coming?” A packing planner stores items and answers “what haven’t I packed?” The moment an app has to answer two unrelated questions, it needs two data models, two screens, and roughly four times the testing.

Four properties separate an easy web app to build from a project that stalls:

  • One data type. Guests, items, recipes, or ideas. Not guests and vendors and invoices.
  • No money. As soon as a payment is involved, you inherit refunds, receipts, tax, and failure states.
  • No permissions. If the app doesn’t need to know who’s looking at it, you skip login screens, roles, and password resets entirely.
  • Data you already own. No scraping, no external feeds, no API keys.

This is where AI web app ideas for beginners differ from the classic beginner tutorial. The best apps to build with AI are the ones you can describe in a sentence, not the ones with the longest feature list. With vibe coding, you describe the tool in plain language and the builder generates the interface, the data structure, and the logic behind it. That changes what counts as beginner-sized. The limiting factor is no longer your coding ability. It’s how clearly you can describe one small job.

10 simple web app ideas to build with AI this weekend

Each idea below gives you three things: the boundary of the first version, a starter prompt you can paste into an AI builder, and a success check to run before you call it done. The prompts follow the same five-part structure used in other vibe coding prompts: context, goal, constraints, output, and success criteria. Adapt the details, keep the structure.

1. Event RSVP and guest-list tracker

An RSVP tracker collects names and responses for one event and shows a live headcount. It’s the smallest useful app most people can name, and it replaces a group chat where three people said “maybe” and nobody counted.

First version: one event, a form with name, email, attending (yes/no/maybe), and number of extra guests. One table of responses. A confirmed headcount at the top.

Leave out: multiple events, reminder emails, seating charts, ticket sales.

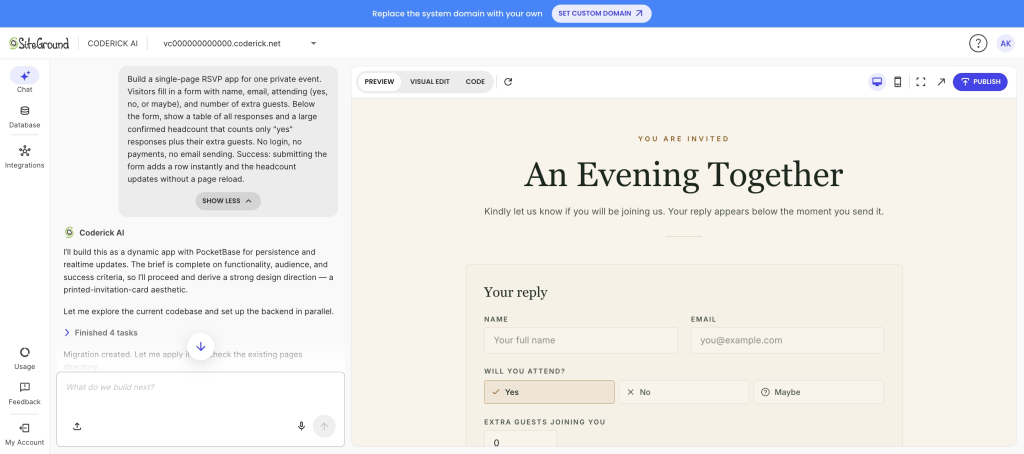
Build a single-page RSVP app for one private event. Visitors fill in a form with name, email, attending (yes, no, or maybe), and number of extra guests. Below the form, show a table of all responses and a large confirmed headcount that counts only “yes” responses plus their extra guests. No login, no payments, no email sending. Success: submitting the form adds a row instantly and the headcount updates without a page reload.

Coderick AI generating an RSVP web app from a natural language prompt with a live preview.

Success check: add 5 test guests including one “maybe” and one with 2 extra guests. The headcount should read 3 higher than the number of yes rows, and the maybe should not be counted.

2. Decision matrix for comparing options

A decision matrix scores options against weighted criteria and ranks them. It’s useful for choosing a laptop, a supplier, or an apartment, and it’s a good beginner app idea because the entire app is arithmetic on a grid.

First version: add up to 6 options as rows, up to 5 criteria as columns, a 1 to 5 weight per criterion, a 1 to 10 score per cell, and an automatic total with the winner highlighted.

Leave out: saving multiple matrices, sharing, templates, collaborative scoring.

Build a single-page decision matrix web app. Users add options as rows and criteria as columns. Each criterion has a weight from 1 to 5. Each cell takes a score from 1 to 10. Calculate a weighted total per option, sort options by total, and highlight the top row. Everything happens on one screen with no accounts. Success: changing any weight or score immediately reorders the ranking.

Success check: enter 3 options, then change one criterion’s weight from 1 to 5. If the ranking doesn’t move when the weight of a criterion you scored unevenly changes, the math is wrong.

3. Household inventory catalog

A household inventory catalog lists what you own, where it is, and what it cost. People build it for insurance claims, moves, or simply to stop buying a fourth pair of scissors.

First version: item name, room, purchase date, value, notes. A filter by room. A total value that reflects the current filter.

Leave out: photo uploads, barcode scanning, warranty reminders, insurance report exports.

Build a household inventory web app. Each item has a name, room, purchase date, estimated value, and a notes field. Show all items in a sortable table with a dropdown filter by room and a total estimated value above the table. The total must reflect the active filter. No image uploads, no accounts. Success: filtering to one room updates both the visible rows and the total.

Success check: enter 15 items across 3 rooms, then filter to the room with the most expensive item. The total has to drop, and it has to match the sum of the visible rows.

4. Reading or watchlist tracker

A watchlist tracker holds the books, films, or courses you mean to get to and moves them through three states. It’s one of the most common beginner web app project ideas because every list app you’ve tried is either too heavy or wants an account.

First version: title, type, status (want to start, in progress, finished), a 1 to 5 rating on finished items, and one short note. Two views: “up next” and “finished”.

Leave out: importing from external catalogs, cover art, friends, recommendations, reading streaks.

Build a personal watchlist web app. Each entry has a title, type (book, film, or show), status (want to start, in progress, finished), an optional rating from 1 to 5, and a one-line note. Show two tabs: “Up next” listing everything not finished, and “Finished” listing finished items sorted by rating. Status changes with one click from the row. No accounts, no external data sources. Success: marking an item finished moves it out of “Up next” and into “Finished” immediately.

Success check: mark an in-progress item as finished. It should disappear from “up next” in the same click, without a refresh.

5. Trip packing planner

A packing planner turns “did I pack the charger?” into a checklist you reuse for every trip. It’s the easiest of these apps to test, because the test is whether your checkmarks survive closing the browser.

First version: items grouped into 4 or 5 categories, a checkbox per item, a progress count, and a “clear all checks” button so the list is reusable.

Leave out: weather lookups, multiple simultaneous trips, shared lists, per-person packing.

Build a reusable trip packing checklist web app. Items are grouped under categories such as Clothes, Toiletries, Tech, and Documents. Each item has a checkbox. Show a packed count like “12 of 25 packed” at the top. Include a button to reset all checkboxes for the next trip, and let users add or delete items. Checked state must persist between visits. No accounts. Success: checking items, closing the browser, and returning shows the same items still checked.

Success check: check 10 of 25 items, close the tab, and open the app again. If the checks are gone, the app isn’t saving data. It’s redrawing it.

6. Recipe organizer and meal shortlist

A recipe organizer stores the meals you actually cook and builds a shopping list from the ones you pick for the week. This is where a small app beats a notes file, because a notes file can’t combine ingredients.

First version: recipe name, tags, ingredient list, and a “shortlist” toggle. One combined shopping list built from the shortlisted recipes, with duplicate ingredients merged into a single line.

Leave out: nutrition data, serving-size scaling, cooking instructions, grocery integrations.

Build a recipe organizer web app. Each recipe has a name, up to 3 tags, and a list of ingredients as free text lines. Users can toggle any recipe into a weekly shortlist. Generate a combined shopping list from all shortlisted recipes, merging identical ingredient names into one line with a count of how many recipes need them. No nutrition data, no accounts. Success: shortlisting two recipes that both need onions shows onions once, marked as needed by 2 recipes.

Success check: shortlist 3 recipes that share an ingredient. That ingredient must appear exactly once in the shopping list. If it appears three times, the merge logic didn’t happen.

7. Content idea organizer

A content idea organizer holds post ideas with their hook, channel, and status so they stop living in six different places. It’s one of two lightweight business tools on this list, and it stays small because it never touches a publishing API.

First version: idea title, channel, hook (one line), status (idea, drafting, scheduled, published), and target date. A board or table grouped by status with a count per group.

Leave out: publishing to social platforms, performance analytics, team assignment, approval workflows.

Build a content idea organizer web app. Each idea has a title, channel (blog, newsletter, or social), a one-line hook, a status (idea, drafting, scheduled, or published), and a target date. Group ideas by status with a count in each group heading, and let users change status from the idea itself. Sort within each group by target date, soonest first. No external publishing, no accounts. Success: changing an idea’s status moves it to the correct group and updates both counts.

Success check: move an idea from “idea” to “drafting”. Both group counts must change in the same action. One count moving is a partial update, which is a bug you’ll otherwise find weeks later.

8. Feedback and idea-voting board

A voting board collects suggestions and lets people upvote them, so the loudest request stops being the one that arrived most recently. Keep it to one board and it stays a weekend project.

First version: submit an idea with a title and one-line description, an upvote button per idea, a sort by votes, and a simple one-vote-per-browser check.

Leave out: accounts, comments, moderation queues, public roadmaps, status labels.

Build a public idea voting board web app. Anyone can submit an idea with a title and a one-line description. Each idea shows an upvote button and a vote count, and the list sorts by votes with the highest first. Prevent the same browser from voting twice on the same idea by storing votes locally. No accounts, no comments, no moderation. Success: voting twice on the same idea from the same browser increases the count only once.

Success check: vote on the same idea twice from one browser, then once from a different browser or a private window. The count should go from 0 to 1 to 1 to 2.

9. Simple quote or estimate calculator

A quote calculator turns your pricing rules into a form that produces a number. It’s the most immediately useful of these no-code app ideas for anyone who currently answers “how much?” by opening a spreadsheet.

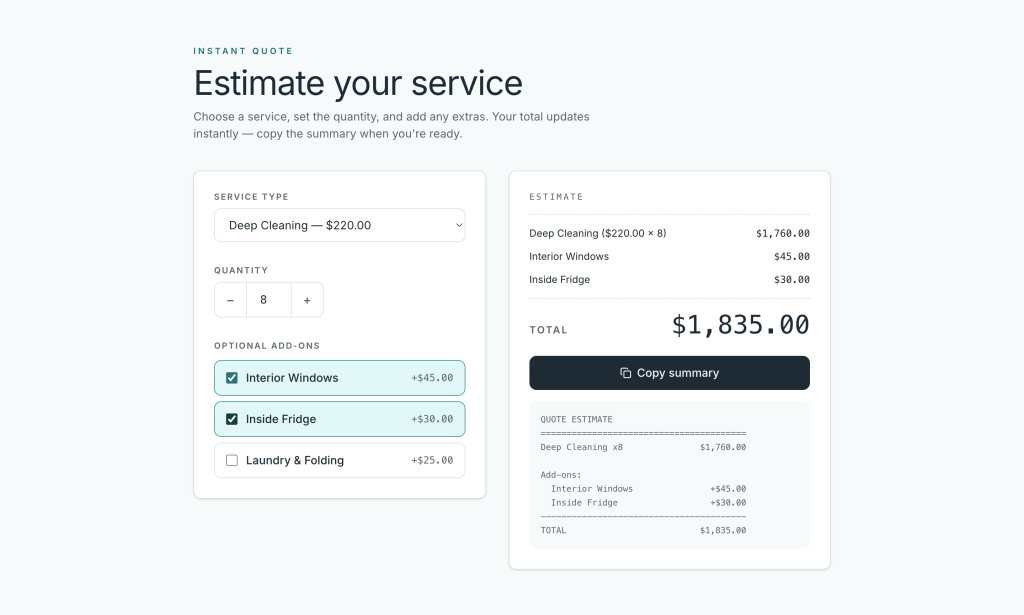
First version: service type, quantity, up to 3 add-ons with fixed prices, and a total with a plain-text summary the visitor can copy. Prices live in the app. No payment.

Leave out: taking payment, invoices, client accounts, regional tax rules, saved quotes.

Build a quote estimate calculator web app for a service business. The form has a service type dropdown with 3 options at fixed base prices, a quantity field, and 3 optional add-on checkboxes with fixed prices. Show a running total that updates as the visitor changes any field, plus a copyable plain-text summary listing every line item and the total. Do not collect payment or personal data. Success: the total always equals base price times quantity plus the checked add-ons.

Success check: run 3 jobs you’ve actually quoted in the past 6 months through the calculator. If any result is more than 10% off what you charged, your pricing rules aren’t what you thought they were, which is worth knowing before a client uses the form.

Web app quote calculator with service selection, optional add-ons, quantity controls, and an automatically calculated total.

10. Plant-care or habit tracker

A recurring-task tracker records when you last did something and tells you what’s due today. Watering plants is the friendly version. It works identically for filters, medication reminders, or a workout schedule.

First version: item name, frequency in days, last-done date, and a “due today” list at the top. One button per item that sets last-done to today.

Leave out: push notifications, streaks and badges, multiple users, photo logs.

Build a recurring care tracker web app. Each item has a name, a frequency in days, and a last-done date. Calculate the next due date from the last-done date plus the frequency, and show a “Due now” section at the top listing every item whose due date has passed. Each item has a “Done today” button that sets last-done to today’s date and moves it out of the due list. No notifications, no accounts. Success: an item with a 3-day frequency last done 4 days ago appears in “Due now”.

Success check: create an item with a 3-day frequency and backdate the last-done field by 4 days. If it doesn’t appear as due, the date math is off by a day, which is the single most common bug in this app.

How to choose which web app idea to build first

Pick the idea whose data already exists somewhere you can copy from in 10 minutes. That’s the whole decision. If the guest list is in your phone, build the RSVP tracker. If your pricing rules are in a spreadsheet, build the quote calculator. An app you can fill with real data on day one gets tested honestly. An app that needs invented data gets admired and abandoned.

Three filters, in order:

  1. Will you use it within 7 days? A packing planner before a trip gets used.
  2. Do you already have 20 real entries? Twenty rows is enough to expose bad sorting, broken filters, and layouts that only work with three items.
  3. What happens if it’s wrong? A miscounted headcount is an inconvenience. A wrong invoice is a problem. Start where mistakes are cheap.
If you want toBuildData it storesReusable after?
Organize a personal eventRSVP and guest-list trackerNames, responsesYes, per event
Make a hard choiceDecision matrixOptions, weighted scoresYes, any decision
Prepare for insurance or a moveHousehold inventory catalogItems, rooms, valuesOngoing
Stop losing track of mediaReading or watchlist trackerTitles, statuses, ratingsOngoing
Travel without forgetting thingsTrip packing plannerItems, checked stateYes, every trip
Plan the week’s cookingRecipe organizerRecipes, ingredientsWeekly
Keep creative work movingContent idea organizerIdeas, status, datesOngoing
Prioritize customer requestsFeedback and voting boardSuggestions, votesOngoing
Answer pricing questions fasterQuote calculatorPricing rulesOngoing
Remember recurring tasksPlant-care or habit trackerItems, frequency, datesOngoing

Tool choice matters less than scope, with one exception: whether the app can save data without you setting up a database. A tracker that forgets everything on refresh isn’t a tracker. An AI website builder that works without code and generates its own backend removes that step, which is the difference between a working app and a pretty mockup.

What to leave out of your first version

Cut every feature that requires a second screen. Most beginner web app projects fail on scope, not on prompting, and the same four features are responsible: user accounts, payments, notifications, and file uploads. Each one brings its own error states, and error states are where beginners run out of weekend.

What to leave out, and what to do instead:

  • User accounts. Instead, keep the app private by keeping the URL private. Add authentication in version 2, once you know the app is worth logging into.
  • Payments. Instead, output a total and a copyable summary. Take the money the way you take it now.
  • Notifications. Instead, show a “due now” or “waiting on you” section at the top of the screen. The app tells you when you open it.
  • File and photo uploads. Instead, use a text field for the detail you’d have captured in the image, such as a serial number or a link.
  • Multi-user editing. Instead, one person edits and everyone else reads.

There’s a practical reason to be strict here beyond time. Every refinement prompt spends some AI tokens, and simpler prompts consume fewer of them. A tight first version leaves you tokens to fix what testing reveals. A sprawling first version spends them arguing with a login screen you didn’t need. This is the most common of the AI app builder mistakes beginners make, and it happens before a single prompt is written.

How to test a small web app before anyone else sees it

Run five checks in this order. They take about 10 minutes together and they catch nearly everything that goes wrong in an app this size.

  1. The empty state. Load the app with zero entries. It should say something useful, not show a broken table or a total of NaN.
  2. Twenty real entries. Paste in actual data, not “test test test”. Real data has long names, missing fields, and duplicates, and it breaks layouts that three tidy rows never will.
  3. The refresh test. Enter data, close the tab, reopen the app. Anything that disappears was never saved.
  4. The phone test. Open it on your phone. Tables are the usual casualty. If you can’t read a row without pinching, the app needs a stacked layout on narrow screens.
  5. The wrong-input test. Type a word in a number field. Leave a required field blank. Enter a date in the past. The app should refuse politely instead of crashing or saving nonsense.

Fix one thing per prompt. Bundling five fixes into one instruction makes it hard to tell which change caused which result, and it’s how working features get quietly overwritten. Version control and staging exist for exactly this: if a refinement makes things worse, revert to the last good version instead of prompting your way back out. Testing in small loops like this is the core of a repeatable vibe coding workflow, and it’s what separates a build that survives contact with real users from one that doesn’t.

When all five checks pass, show it to one person who wasn’t involved. Watch them use it without explaining anything. Whatever they hesitate over is your version 2 list, and it will be shorter and more accurate than the feature list you would have invented on your own.

Start with one idea this weekend

Any of these 10 simple web app ideas is small enough to go from prompt to working app in a weekend, provided you hold the line on scope. One data type, one screen, no payments, and 20 rows of real data to test against. The idea that gets finished is almost never the most ambitious one on the list. It’s the one whose data you already had.

You can build any of them with Coderick AI, which turns a plain-language description into a working app with hosting, SSL, a generated backend, and version control included from the first prompt. Access comes with a SiteGround hosting plan, the only thing left to decide this weekend is which of the 10 ideas you’ll actually use.

[96]


Frequently asked questions (FAQ)

What are some simple web app ideas I can build with AI?

Simple web app ideas that work well with AI builders include an RSVP and guest-list tracker, a weighted decision matrix, a household inventory catalog, a watchlist tracker, a trip packing planner, a recipe organizer, a content idea organizer, an idea-voting board, a quote calculator, and a recurring-task tracker. All 10 store one type of data and answer one question about it.

What web apps can beginners build without coding?

Beginners can build any simple web app without coding that collects, organizes, or calculates data without needing payments, logins, or outside services. Trackers, checklists, calculators, and simple catalogs all qualify. You describe the tool in plain language, and the builder generates the interface and the data structure for you.

Which web app ideas can be finished in a weekend?

Web app ideas for beginners that can be finished in a weekend have one data type, about 5 fields, and one or two views. A packing checklist, a decision matrix, or a quote calculator fits comfortably. Anything with user accounts, payments, or multiple connected record types does not, regardless of how simple the pitch sounds.

How do I choose a simple web app idea?

Choose the idea whose data you can copy from somewhere in 10 minutes and that you’ll use within the next 7 days. Those two conditions matter more than how interesting the idea is, because they’re what get the app tested with real information instead of placeholder rows.

What should a beginner web app include?

A beginner web app should include one input form, one list or table view, one calculated summary such as a count or total, and data that persists after a refresh. That’s the complete requirement. Everything else is version 2.

What features should I leave out of my first web app?

Leave out user accounts, payments, notifications, file uploads, and multi-user editing. Each one adds error states that take longer to handle than the core app itself. Keep the app private by keeping the URL private, and output a copyable summary instead of processing payments.

Can Coderick AI build a web app from a prompt?

Yes. Coderick AI builds a web app from a plain-language prompt, then refines it through continued chat instructions. It generates the interface and the backend together, and includes hosting, SSL, custom domains, user authentication, and version control on paid plans, so there’s no separate infrastructure to configure. 

How should I test a small AI-built web app?

Test a small AI-built web app in five passes: load it empty, add 20 real entries, refresh to confirm data was saved, open it on a phone, and feed it wrong input such as text in a number field. Fix one problem per prompt so you can tell which change fixed what.

AI plugin fragmentation in WordPress: Why more choice makes sites harder to manage

Count the WordPress AI plugins on your site. If there are more than two, you probably didn’t plan it that way. One arrived to write meta descriptions, another to answer visitor questions, a third because the first couldn’t do images. Each install solved the problem in front of you.

What comes next is AI plugin fragmentation in WordPress: the AI capabilities you need spread across several narrow tools, none of them aware of the others, and the work of holding it all together left to you. Our 2026 report on AI in WordPress for small businesses found 67% of small business owners doing that work alone, wasting time they could use to run their actual business.

Key takeaways:

  • AI plugin fragmentation in WordPress is a supply problem before it’s your problem. A new AI plugin joins the WordPress directory roughly every 1.8 hours.
  • The cost is never the sticker price. Each plugin adds a settings screen to learn, an update cycle to keep up with, and a share of your security exposure. Many also add an account, a key, and a subscription of their own.
  • Plugins are where the security risk sits. Most of the WordPress vulnerabilities disclosed most recently were in plugins.
  • WordPress 7 fixed part of this and moved the rest. Developers got one standard way to reach AI providers. Site owners still create accounts, generate keys, and watch token bills.
  • The goal is fewer connections, not fewer capabilities. Consolidation is about reducing the number of things you maintain, not giving up what they do.

What AI plugin fragmentation in WordPress means

Fragmentation is what happens when a job gets divided across tools that were never designed to work together. In WordPress, it means one AI plugin writes your content, a second handles SEO metadata, a third runs a chatbot, and a fourth generates images, with no shared account, no shared settings, and no shared idea of what your site is for. You’re the only thing connecting them.

This isn’t a failure of judgment on your part, but rather the shape of the supply. An independent count of the entire WordPress plugin directory, published in July 2026 by WordPress consultant Casey Burridge, found 3,163 AI plugins among 68,651 listings, with 17.4% of everything added in 2026 being AI-related. That’s roughly one in six new plugins.

The first 1,000 AI plugins took WordPress.org 18.3 years to accumulate. The second thousand took 9.4 months, and the third took 88 days. Two-thirds of every AI plugin ever listed arrived in the last twelve months. Our own 2026 report on AI in WordPress for small businesses puts the growth rate at roughly three times faster than the wider plugin economy.

More supply isn’t the same as more help. As the author of that count puts it, one in six being AI-related is a supply signal rather than a quality signal, spot checks suggest plenty are thin wrappers around somebody else’s API key, and discovery in the directory was already hard before this. Meanwhile, 44.4% of the small business owners in our report already name finding and configuring plugins as one of their biggest difficulties. The shelf got fuller for people who were already struggling to choose from it.

What stacking narrow WordPress AI plugins actually costs you

Listicles price WordPress AI tools for small business one at a time, which is exactly how the total escapes notice. Here’s what each one adds, beyond its monthly fee.

CostWhat it looks like in practiceWhy it compounds
CredentialsAn API key to generate, paste in, and keep track of for each AI plugin that talks to a providerEvery key is a credential to store, rotate, and eventually lose track of. Losing track is the normal outcome, not the unusual one
SubscriptionsSeparate billing for each narrow tool, with token charges underneathFour tools at typical plugin subscription prices is not a small line, and token spend moves on top of it every month
InterfacesA different settings screen and a different mental model per pluginSomeone already finding the WordPress dashboard difficult now has five more dashboards inside it
Update cyclesEach plugin ships on its own schedule with its own breaking changesMore update surface means more weekly maintenance and more chances that a conflict takes the site down
Security surfaceEach plugin is code with permissions, often handling API tokens and exposing endpointsPlugins accounted for 91% of WordPress vulnerabilities disclosed in 2025. Every addition widens the surface
OverlapTwo plugins doing similar work, neither doing it completelyYou pay twice and still have a gap, which is usually what prompts installing the sixth

The overlap described in the last row happens for a reason that has nothing to do with choosing carelessly. The plugins you already run are adding AI of their own. For example, Rank Math and Yoast added AI writing to their SEO panels, Elementor added it to the page builder, and the translation plugins added AI translation. So the AI plugin you install to write product descriptions may duplicate something the SEO plugin you’ve had for three years gained in an update you never read the notes for.

Keep in mind: The directory’s search is showing you tags, not capabilities. Plugin authors choose their own tags, and many carry several. A tool tagged for chatbots, SEO, ecommerce, and content will surface for all four searches while doing one of them well. Before installing, read the changelog rather than the description. The description is marketing; the changelog shows what has actually been built and when anyone last touched it.

Did WordPress 7 solve AI plugin fragmentation?

WordPress 7.0 partly solved AI plugin fragmentation, and this is the part most coverage gets wrong in one direction or the other. It was built to address exactly this problem, and WordPress 7.1 continued the work at the same layer. It succeeded there, but it just wasn’t the layer where you live.

What the AI Client and Connectors screen fixed

Before WordPress 7, every plugin that wanted to use AI wrote its own connection code for every service it supported. Dozens of plugins each maintained their own integrations, and credentials ended up scattered across as many settings screens as you had plugins.

WordPress 7 replaced that with a shared foundation. The AI Client gives plugins one standard way to ask for what they need, and WordPress routes the request to whichever provider you’ve connected. The Connectors screen puts provider credentials in one place instead of many. Within months, more than 70 plugins had registered with the new layer. If you want the details, our explainer on how AI works in WordPress 7.0 covers it.

One condition decides whether any of that reaches you. The sharing only applies to plugins built to use Connectors. A plugin that predates WordPress 7, or that simply keeps its own settings screen, still stores its own key exactly as before. And if you’re still on WordPress 6.x, none of it applies yet, because the Connectors screen isn’t there: every AI plugin carries its own key. Adoption is early, so on most sites today the answer is mixed: some tools share a provider connection, others carry their own.

Why the AI plugin fragmentation moved to the provider level

What WordPress 7 standardized was how plugins reach AI providers. What it didn’t change is the WordPress AI plugin setup complexity you face before any of that helps. You still open the Connectors screen, choose a provider, install that provider’s plugin, create an account on the provider’s website, find your way into its developer dashboard, generate an API key, come back and paste it in, and then install a separate features plugin before anything visible appears. After that you track spending in the provider’s own billing dashboard.

Then there’s the catch that turns one setup into two. Providers don’t all do everything. For instance, Anthropic’s models generate text but not images, so an owner who needs both connects a second provider, which means a second account, a second key, and a second billing dashboard to watch.

So WordPress 7 solved fragmentation for developers and moved it to the provider layer for everyone else. The count genuinely improved: instead of entering the same key into five plugin settings screens, you enter it once, and every plugin sharing that connector uses it. What didn’t improve is the work in front of that. You still create the account, generate the key, install two plugins, and watch a billing dashboard, and needing both text and images means doing all of it twice.

When multiple WordPress AI plugins are the right answer

Consolidation arguments can read as sales copy when they pretend there’s never a reason to run several tools. There are actually three cases when it’s worth it to choose multiple WordPress AI plugins:

  • If a specialized AI plugin genuinely beats a more general one. Things like industry-specific compliance are deep problems, and a tool built for one of them will do it better than a broad platform. If your business depends on that depth, pay for it.
  • If you already rely on the tool and it works. If your trusted SEO plugin added AI features and your whole workflow runs through it, replacing it to reduce a count isn’t a saving. There can be switching costs, and consolidation for its own sake isn’t a goal.
  • If the requirement is genuinely narrow. One small job, one small plugin, no ongoing cost, no credential: if this is what you use your AI plugin for, then there’s no need to replace it.

The test is whether each one of your AI plugins is there because you chose it for a job, or because it was the fastest answer to a problem you had on a random Tuesday.

Pro tip: Sort your list by last updated, not by name. In your Plugins screen, the useful question isn’t what each tool does but whether anyone is still maintaining it. A plugin that hasn’t shipped an update in a year is carrying whatever security issues it had a year ago, and abandoned AI plugins are especially common because many were built quickly during the rush described above. Anything unmaintained that also holds an API key is the first thing to remove, because it combines the two risks in this article into one line on your site.

How to reduce WordPress AI tool sprawl

To avoid AI plugin fragmentation in WordPress, consolidate by reducing connections, not capabilities: one place that reaches your site, one set of credentials, one interface to learn, one record of what changed.

A site-connected AI agent can reduce WordPress AI tool sprawl this way. For example, SiteGround’s AI Agent for WordPress connects once and then handles content, media, plugins, users, and WooCommerce through the same conversation, with no provider account to create and no key for you to store.

A screenshot of the AI Agent by SiteGround dashboard featuring the central heading "How can I help you today?" and the tagline "Your WordPress AI Assistant. Ask about content, your store, speed, or security." Below the blue icon logo sits a prompt input box with the placeholder text "Ask me anything WordPress related and I'll help." Category tabs beneath the input highlight "Most Popular" alongside options for "Create & Manage Content," "Optimize & Protect," and "Store," followed by suggested starter prompts: "Write an SEO-friendly blog post with AI images and headings," "Run a full SEO audit of my site," and "Speed up my site automatically (with SiteGround Speed Optimizer)."

You don’t have to replace everything at once, and it’s usually a mistake to try. Stop the stack growing first, then replace the tools whose jobs already overlap, and keep the specialists that earn their place. Our guide to AI plugins and AI agents covers that choice in more detail.

Whichever route you take, count the things you maintain rather than the AI features you have.

The problem was never a shortage of WordPress AI plugins

AI plugin fragmentation in WordPress isn’t caused by bad plugins or by careless site owners, but rather by a directory adding a new AI plugin every 1.8 hours, aimed at people who mostly manage their sites alone, in a market where each tool solves one slice and none of them can see the others.

So before the next install, ask what it adds to the list of things you now have to keep working: another screen, another update, and often another account, key, and bill. Answer that, and the right number of WordPress AI plugins usually turns out to be smaller than the number you have. And you might also be surprised by how much of your AI needs you can consolidate with a single AI Agent.

FAQs

What is AI plugin fragmentation in WordPress?

AI plugin fragmentation in WordPress is when the AI capability a site needs ends up spread across several narrow plugins, each with its own settings screen and update cycle, and often its own account, API key, and subscription, with none of them aware of the others. The work of holding them together falls to the site owner.

Why are multiple WordPress AI plugins hard to manage?

Multiple WordPress AI plugins are hard to manage because each one adds a separate interface and update schedule, and often its own credential and billing relationship. The features add up, but so does the maintenance, and 44.4% of small business owners already report difficulty finding and configuring plugins.

What security risks come from stacking multiple WordPress AI plugins?

The risks of stacking multiple AI plugins are a wider security surface, conflicting code, duplicated spending, and credentials nobody is tracking. Plugins accounted for 91% of WordPress vulnerabilities disclosed in 2025, and AI plugins often hold API keys that can spend money.

Why do WordPress AI plugins need API keys and add subscription complexity?

WordPress AI plugins need API keys and can add subscription complexity because most do not include the AI itself. They connect to an outside provider through an account you create and pay for separately, so each plugin can mean another key to store and another bill to watch.

Did WordPress 7.0 solve AI plugin fragmentation?

WordPress 7.0 solved AI plugin fragmentation partly. It standardized how plugins reach AI providers and centralized credentials in the Connectors screen, which fixed the problem for developers. Site owners still create provider accounts, generate keys, install a features plugin, and monitor token billing, so the fragmentation moved to the provider layer rather than disappearing.

How can site-connected AI agents reduce WordPress AI tool sprawl?

Site-connected AI agents reduce WordPress AI tool sprawl by replacing several narrow plugins with one connection, one set of credentials, and one interface. Instead of maintaining separate tools for content, media, and store tasks, you work through a single agent connected to the site.

How to build internal tools with AI for your business without coding

A man holding a laptop uses an AI prompt to create an "Internal dashboard" that is shown floating on the right. The user's prompt is: "Create a dashboard to track our project status..." Below the prompt, a loading state shows: "Generating..." The resulting AI-generated dashboard displays project statistics for "This week": 12 active projects, 8 completed, and 3 at risk. A detailed project table lists projects with columns for Project, Owner, Status (e.g., On track, In progress, At risk), Priority (e.g., High, Medium), and Due date.

Somewhere in your business there’s a process running on a spreadsheet, three email threads, and someone’s memory. Maybe it works most of the time, but it also breaks the same way every month: two people edit the same row, a request stalls because nobody owned it, and the status column means different things to different people.

An internal tool replaces that with one place where the records live, the statuses are agreed, and each person sees the part that concerns them. You can now build internal tools with AI by describing the process instead of coding it or hiring a programmer, which moves the work from writing software to defining what your team actually does.

Key takeaways:

  • Start with your records, not with a platform. What you track, what states it moves through, and who can do what. Platform roundups answer a question you don’t have yet.
  • Eight elements make a specification build-ready. Users, records, actions, states, permissions, views, exceptions, and a success test.
  • You can build internal tools with AI without coding. What decides the result is the description you write, not the software you write it into.
  • Exceptions are the most skipped element and the one that decides whether the tool survives. Missing fields, duplicates, late items, and rejections happen in week one.

Dashboards, CRMs, and admin panels are the same system

If you search for the best internal tools, you’ll find dashboards in one roundup, CRMs in another, and admin panels in a third, as though you have to pick a category before you start. You don’t, because they aren’t different kinds of software. They’re different windows onto the same one.

Underneath each sit records, the individual things you track, and states, the stages those things move through. A CRM is a records view with a sales pipeline as its state model. A dashboard is the same records counted and summarized. An admin panel is those records again, opened for editing by people you trust with that. So when you set out to build a CRM with AI, or go looking for a dashboard builder, you are describing the same system twice.

This changes the question. You stop asking whether you need a dashboard or a CRM and start asking what your records are and what states they move through. Answer that once and the views follow. Most no-code internal tools are business process tools at heart, and a team that defines its records properly gets all three views without building three things.

Start with the process, not the platform

Nearly every guide on this subject opens with a ranked list of builders. That’s the wrong first question, and not only because most of those lists are published by the platforms on them. It’s the wrong question because the obstacle is rarely the tool. Most small businesses have never written down how their own process works.

This is also why non-technical teams that build internal tools without code are sometimes disappointed. Given a vague description, a builder produces a plausible, generic app that matches nothing in particular. But given a precise one, it produces something your team recognizes. The quality of what comes out tracks the quality of what went in, and the input is a specification you write, not a platform you choose.

If you haven’t settled on a builder yet, take a look at our guide to choosing a no code web app builder.

Eight questions that turn a process into an internal tool specification

Answered in order, the following eight elements turn an informal business process into an internal tool specification a builder can act on. Work through them against your own process rather than just reading them.

ElementThe question Why it matters, and what goes wrong without it
UsersWho uses the tool?Decides how many views you need. Teams design for themselves and forget the person who only submits a request and never opens anything else
RecordsWhat information does it store?The unit of work: a job, a lead, an invoice, a request. Getting this wrong at the start makes everything after it wrong
ActionsWhat can each user do?Create, edit, approve, assign, close. Actions are where permissions and workflow meet
StatesHow does work move through the process?The status field is the process. Most spreadsheet workflows already have states, in a column nobody formally agreed on
PermissionsWho can view, edit, approve, or delete?The difference between a tool a team trusts and one where somebody deletes a month of records
ViewsWhat does each user need to see?This is where dashboards, board layouts, and admin screens come from. They’re outputs of the model rather than choices you make up front
ExceptionsWhat happens when information is missing, invalid, late, duplicated, or rejected?The most skipped element, and the one that decides whether the tool survives contact with real data
Success testWhat proves version one is useful?Defined before building. Usually: the team stopped using the spreadsheet

Take for example a team handling internal purchase requests through a shared sheet and an inbox. Here’s how the eight answers come out.

  • Users. Anyone who can request something, the two managers who approve, the director who signs off on anything large, and the office administrator who orders and receives.
  • Records. Requests, each holding an item, a cost, a reason, a requester, and a date needed.
  • Actions. Submit, approve, reject, mark ordered, mark received.
  • States. Submitted, approved, rejected, ordered, received.
  • Permissions. Requesters see only their own and approve nothing. Managers approve up to a limit and pass anything larger to the director. The administrator edits any request and deletes none.
  • Views. A requester sees a form and their own history. A manager sees a queue of pending approvals. The director sees monthly totals by team, which is the dashboard nobody had to specify separately.
  • Success test. The sheet stops being updated within a month.
  • Exceptions are where the real work is. What happens when a request arrives with no cost attached, when the same item is requested twice in a week, when an approval sits untouched for five days, and when a rejected request gets resubmitted with a different number? Each answer is a rule the builder needs. The success test is that the sheet stops being updated within a month.

Your states are already written down, in the messiest column of your spreadsheet. Before inventing a status list, sort that column and read every distinct value people have typed into it. You’ll find the official ones, and you’ll also find the informal ones: “waiting on Dave,” “chasing,” “held until budget.” Those are states your process has and nobody ever agreed on, which is exactly why work gets stuck in them. Deciding which to keep and which to merge is most of the states question, already done for you.

How to build internal tools with AI from your specification

With those eight answers written down, the build step is mostly transcription. You describe the tool to an AI internal tool builder in plain language, in the order of the model. A useful description names the records, the states, who does what, and one exception rule, rather than asking for a category of app.

So rather than just saying “build me an internal purchase request app”, which will just result in the AI builder guessing what you need, your initial vibe coding prompts can be something specific like this:

“Build a purchase request tool. Each request stores an item, cost, reason, requester, and date needed, and moves through submitted, approved, rejected, ordered, and received. Requesters see only their own requests. Managers approve up to $500 and anything higher goes to the director. Flag any request submitted without a cost instead of accepting it.”

If you give this prompt to an advanced AI builder like Coderick AI, what comes back is a working internal tool rather than a mockup:

A screenshot of a web application preview displaying a login page split into two sections beneath a top editor bar with a blue "PUBLISH" button. The left dark panel features the "Ledger" logo, the headline "Every purchase, on the record.", a description for an internal procurement workspace, and a "manager limit" badge. The right light panel shows a "Welcome back" sign-in form with email and password input fields, a dark "Sign in" button, and a "No account? Create one" link.

Coderick AI generates the database behind it with the fields you named, created the three roles, and built a separate view for each: requesters see their own requests, approvers get an approval desk with a queue of what’s waiting on them specifically, and everything moves through the status pipeline you defined. The approval limits are enforced in the data rather than just in the interface, and the exception rule comes back with a recovery path, since flagged requests give the requester an “Add cost” action instead of leaving them stuck. It also makes the design decisions you left out, which at this stage is very welcome.

From there, you can refine your internal tool (see our guide to vibe coding workflows for more insights on how to do it). When the version in front of you is right, publishing takes one click. Your tool goes live with hosting included, so there’s no separate deployment step and nothing to set up before your team can log in.

How to test an AI-built internal tool before your team depends on it

Your instinct might be to check that the AI-built internal tool works. But what matters more is whether it holds up when the process misbehaves, which is what week one will do to it. Most of the AI app builder mistakes that surface later are visible in the first hour if you test for the right things.

  • Use real, messy data, not clean examples. Take fifty rows from the actual spreadsheet, including the incomplete ones and the ones with a note typed into a number field. A tool that only works on tidy input isn’t ready.
  • Run every exception you wrote down. Submit a request with a field missing. Submit the same one twice. Leave an approval untouched past its deadline. Reject something and resubmit it. You defined what should happen in each case, so check that it does.
  • Test each role as that person, not as yourself. Log in as a requester and try to approve your own request. Log in as a manager and try to exceed the limit. Permissions that were described correctly can still be built loosely, which is one of the checks our guide on whether vibe coding is safe covers in more depth.
  • Check the success test you set. Not whether the tool looks finished, but whether the team stopped updating the spreadsheet. That’s the only result that tells you it worked.

Pro tip: Test with the person who submits, not the person who built it. Whoever writes the specification tests the manager and admin views hardest, because those are the ones they thought about most. The requester view gets tested last and used most, by people who never see the rest of the tool. Hand it to someone who only submits requests, give no instructions, and watch where they hesitate. Every hesitation is a label or a missing option you’d never find from the inside.

When to buy software instead of building an internal tool

There are processes where building is the wrong call, and knowing which is worth more than any feature list. Almost all build-versus-buy guidance is published by companies with a stake in the answer: platform vendors argue for building, and software management firms argue for buying. Read both, and notice which direction each one leans.

Build when the process is genuinely yours

Building is the right call when the workflow is specific to how you operate rather than to your industry, when no vendor models it without you contorting your process to fit, and when the tool is narrow enough that maintaining it stays small. The purchase-request example qualifies. The approval limits, the roles, and the exception rules are yours, and there’s not much surface area to keep working.

Buy when the function is a commodity

Buying an internal tool wins when the category is mature with credible vendors, when your requirements are pretty standard, and when configuring an existing product already covers the workflow. Payroll, accounting, and email marketing are commodities. Building one to avoid a subscription can be a decision you’ll be servicing for years.

If a workflow hasn’t changed in two years and probably won’t, buying stays the better answer even when no product fits perfectly, because maintaining custom software for a stable process rarely pays back.

Keep in mind that AI-generated software still needs an owner, tests, and updates as the things around it change. AI changed what it costs to build, not what it costs to keep. When the tool gets adopted, small bugs accumulate, and whoever built it becomes its unofficial product owner, fielding requests they never signed up for. That’s survivable when the tool is narrow and expensive when it isn’t, which is the real argument for keeping version one small.

The hard part was never the building

For most of the time internal tools have existed, the barrier was engineering. You knew what your team needed and couldn’t get it made, so the spreadsheet stayed. That barrier has largely gone, revealing the one underneath: most teams have never written down how their own process works.

So when you build internal tools with AI, the eight questions covered here are the work. A team that can answer them has a tool worth building. A team that can’t gets a plausible app matching nothing they do, whatever they build it with.

The next step costs nothing. Open the spreadsheet your process runs on and answer the eight questions against it. Most of it is already there: the columns are your records, the status column is your states, and the people who edit the sheet are your users and permissions. What you’ll be missing is usually the exceptions and the success test, which are the two that decide whether the tool survives.

Once you have your answers, the first version of your AI-built internal tool is one prompt away.

[96]

FAQs

How do I build an internal tool with AI?

You build an internal tool with AI by describing your process precisely enough for the builder to act on it. Define your users, records, actions, states, permissions, views, exceptions, and a success test, then hand that specification to the builder rather than starting from a template.

What should I include in an internal tool prompt?

An internal tool prompt should include who uses the tool, what records it stores, what each user can do, the statuses work moves through, who can view or edit or approve, what each user needs to see, what should happen when data is missing, late, or duplicated, and what result will prove version one is useful.

Can a non-technical team build internal tools without coding?

Yes. A non-technical team can build internal tools without coding, because the hard part is describing the process rather than writing the code. The teams that struggle are usually the ones that skipped defining states, permissions, and exceptions.

How do I turn a spreadsheet workflow into an internal app?

You turn a spreadsheet workflow into an internal app by treating each row as a record, the status column as your workflow states, and the people who edit the sheet as your users and permissions. Most spreadsheets already contain the model, just informally.

How should I test an AI-built internal tool?

You should test an AI-built internal tool with real, messy data rather than clean examples, then deliberately trigger the exceptions: missing fields, duplicates, late items, and rejections. Finish by checking your success test, which is usually whether the team stopped using the spreadsheet.

When should I buy software instead of building an internal tool?

You should buy software instead of building an internal tool when the function is a commodity, the category has credible vendors, your requirements are standard, and the workflow is stable year over year. Maintenance costs several times the initial build, and AI lowers the cost of building without lowering the cost of maintaining.

Can Coderick AI build internal tools such as dashboards, CRMs, and admin panels?

Yes. Coderick AI can build AI-powered internal tools such as dashboards, CRMs, and admin panels, which are three views of the same underlying system. Once you have defined your records, states, and permissions, the views follow from that specification.

Can you trust an AI-built online store with customers and payments?

Abstract of an AI-built online store you can trust

You built an online store in an afternoon. It looks great, you pat yourself on the back. But there’s one looming question: are you actually able to charge someone’s card yet? Are AI-built online stores safe for real payments? The answer is yes — if the store passes a payment-readiness check first. 

Key takeaways:

  • Are AI-built online stores safe for real payments? Yes, once you verify eight specific things before launch, not just the design.
  • Test an AI-built store before launch in order: offer, trust signals, policies and data, checkout, mobile, payment status, confirmation, then edge cases.
  • Secure online checkout means card numbers never touch your site’s own code. That’s not a promise, it’s a technical fact.
  • Coderick AI’s Stripe integration handles one-time purchases and subscriptions automatically.
  • A launch checklist only counts if you run it against a real test transaction, not a visual walkthrough.

One thing first: if you haven’t settled on a platform yet, choose the right selling path before working through the rest of this.

Are AI-built online stores safe for real payments?

Yes, but only if you check a specific set of things before you flip the switch on real payments. AI-built store safety comes down to two things: what you actually check yourself, and how much your builder already handles by default. Most of the risk lives in the first part, and that’s what the checklist below walks you through.

Indeed, an AI website builder can produce a complete-looking store in minutes: product pages, a working cart, a checkout button that appears to do its job. But speed and safety solve different problems. A finished-looking store can still fail on:

  • Payment status handling
  • Refund logic
  • A checkout that breaks the moment someone opens it on a phone

A few things make AI-built store risks a distinct category, not just the standard ecommerce checklist with an AI label stuck on it:

  • AI-generated copy can misstate a price, a shipping promise, or a product spec with total confidence and zero warning.
  • A store built in minutes rarely gets the manual walkthrough an agency-built site would get before launch, because skipping that step was the whole point.
  • The person building it is often not a technical or ecommerce professional either, so there’s no expertise in the loop to catch what a specialist would spot on sight.

None of these problems show up when you’re just poking around a finished site. All three show up the first time a customer tries to pay. That’s why the checklist below treats payment readiness as separate from design readiness.

Heads up: not every AI builder leaves all of this on you. Coderick AI closes off a chunk of it before you even start testing, more on that once you’ve gone through the list below.

AI-built store launch checklist: what to verify before taking real payment

AI-built store payments touch eight separate points before you can actually trust them. Work through each one in order:

1. Start with the offer: is it actually clear?

An AI generator, in all its cheerful optimism, will happily produce a colorful product description, a price, and a delivery promise that don’t quite agree with each other, nevermind what you can actually execute. Before you touch checkout, put yourself in a customer’s shoes landing on this page for the first time. Can they answer:

  • What am I paying?
  • What am I getting?
  • By when?

How to check: read your own product page as a stranger would. If you can’t answer all three in one glance, that’s the fix.

An unclear promise turns into payment risk costs the moment a customer disputes a charge over it. This is also the cheapest fix on the whole list, since it’s a text edit, not a technical one, so do it before anything else here.

2. Do the trust signals actually hold up?

Right after the offer, a customer checks whether you’re a real business with a safe and secure website. This is what they’re looking for:

  • Your business name matches what’s on the payment page.
  • A real contact method exists, and someone actually answers it.
  • Checkout shows a padlock and a recognizable payment brand.
  • There’s a working support channel, not just a contact page that exists for show.

How to check: use your own contact form and support channel like a stranger would, and see whether anything, or anyone, actually answers.

This matters even for businesses that don’t sell physical goods, since the same expectations apply to safe payment pages built for portfolios, restaurants, or one-off event bookings. An AI builder can generate a footer with a contact form in seconds, but it won’t notice if that form points to a dead inbox. 

3. Are your policies actually visible?

Another thing customers expect to see, and that conveys trust, is a clear answer to what happens if something goes wrong, before they hand over a card number, not after. They expect to see:

  • Your refund window is stated plainly, not brushed aside on a page nobody clicks.
  • Your delivery timeline is realistic and accessible before checkout, not just in a shipping confirmation email.
  • Any access or subscription terms are spelled out up front.
Example website with a shipping policy in the footer transmitting trust

How to check: make sure all of these details are easily visible from your product pages, or no more than one click away. 

4. Is the online checkout secure and easy to use?

A secure online checkout comes down to two separate things, and they don’t fail in the same place:

  • Security: this is solved by choosing the right foundation, not by building it yourself. Integrating with a reputable payment processor like Stripe (used as the example throughout this checklist, the same checks apply to whichever one you use) means the most sensitive part of the transaction, the actual card data, is handled by a company that specializes in exactly that: encrypted, PCI-compliant, and built for this one job. It also means checkout carries a brand your customers already trust, rather than an unfamiliar name asking for their card number.
  • Usability: if checkout runs through Stripe’s own hosted page, the payment form itself isn’t something the AI generator built, it’s Stripe’s tested interface. What the AI-built site still controls is everything around it: whether the right product, price, and currency get passed into that page, and whether the redirect back to your site after payment actually works. That hand-off, not the payment form, is where bugs tend to show up.

How to test: place a real test order with a real card, not a made-up test transaction, and confirm the product, price, and currency on Stripe’s page match exactly what you expected before payment.

5. Does checkout actually work on mobile?

We’ve all been there: mobile checkout simply fails in ways desktop checkout doesn’t. And boy is it frustrating. Make sure your mobile experience ticks these boxes:

  • The payment button stays visible instead of hiding under the on-screen keyboard.
  • The card field accepts spaces and other common formatting.
  • The confirmation page loads fully on screen, not cut off at the edge.
online store mobile website that works well and transmits trust

How to test: run the exact same test from step 4, but do it on your phone. AI-generated layouts render cleanly in a desktop preview and only reveal these problems once a thumb, not a mouse, is doing the tapping.

If most of your traffic already arrives on mobile (which, according to recent mobile commerce data, it likely does, with some estimates as high as 78% of global ecommerce traffic), this test matters more than the desktop version you keep checking instead.

6. Does the store know if the payment succeeded, failed, or was canceled?

Can an AI-built store process payments securely? Part of the answer is whether the store actually knows what happened after the customer clicked “pay.” Practically, a payment can:

  • Succeed
  • Fail on a declined card
  • Get canceled mid-checkout

How to test: use your payment processor’s test card numbers to trigger a successful payment, a decline, and a cancellation, then confirm each one redirects to the right place and shows the correct status, both what the customer sees and what your payment processor dashboard reflects.

Your store needs to get this right every time, not just on the happy path, and that consistency is what AI-built store payment security really comes down to.

If you sell subscriptions: run the same test on a renewal charge, not just the first payment. Confirm that a failed renewal actually cuts off access, using recurring access checks rather than leaving the account active by mistake.

7. What happens in the moment right after a customer pays?

Step 6 confirmed a successful payment shows the right status. This step is about whether that moment actually reassures the customer, and two different systems are behind it:

  • Your thank-you page and its next-step messaging come from your own site, not Stripe. Once payment goes through, Stripe hands control back to whatever confirmation page your site built, so a generic “thanks” instead of a real next step is your site’s copy to fix, not a Stripe default.
  • The email receipt is Stripe’s own mechanism, a dashboard toggle, sent from Stripe’s own template.

How to test: place a real test order and time it. Turn receipts on under Customer emails in your Stripe dashboard settings by toggling “Successful payments,” and separately, check that your own confirmation page actually says something useful instead of a generic thank-you.

8. Have you tested what happens when something goes wrong?

The friction-free path is 80% of testing. The other 20% is deliberately breaking things. Let’s get messy.

How to test:

  • Decline a test card
  • Cancel mid-checkout
  • Request a refund
  • Place the same order twice in a row, then check your payment records after checkout to confirm it created one order, not two.

Agencies building AI-generated stores for clients run exactly this kind of client store QA before handoff. If you can’t answer what your store does in each of these four scenarios, you haven’t tested an AI-built store before launch. You’ve only tested that it looks like one.

AreaWhat to check
OfferProduct, service, price, and promise are stated plainly.
Trust signalsBusiness identity, contact information, secure checkout, and a support path are visible.
PoliciesRefunds, delivery, access, and support expectations are clear before checkout.
Customer dataCheckout forms collect only what fulfilling the order requires.
CheckoutA customer can pay without confusion or unexplained errors.
MobileCheckout works cleanly on a phone, not just on desktop.
Payment statusThe store correctly shows success, failure, or cancellation every time.
ConfirmationThe customer gets a clear next step immediately after paying.
Edge casesFailed payments, canceled payments, refunds, and duplicate orders have all been tested.

The checklist above covers what’s specific to AI-built stores. Stripe checks before launch covers what it doesn’t: test mode, live keys, tax, and disputes.

A note on Coderick AI
If you’re building with Coderick AI, SiteGround’s AI website and app builder, checkout and payment status both come included by default, since it connects to Stripe’s own checkout page rather than a payment form built from scratch. A confirmation page comes included too, though its actual messaging (a real next step versus a generic thanks) is still yours to write well, more on that in step 7.
Start building your online store now with Coderick AI>>

What Coderick AI already handles: where a developer still needs to check the rest

A Coderick AI online store comes with a portion of the checklist above already checked off before you typing out any prose on your keyboard.

The security that comes with the site, not just the site itself

Most of the checklist above is about what you test. This part is about what’s running behind the site to keep it safe, none of which a customer ever sees:

  • Access control: user authentication is built in from the start. Weak or missing authentication is one of the most common vulnerabilities found in AI-generated code, so having it handled by default closes off a real, documented gap rather than a hypothetical one.
  • Hosting and security: SiteGround’s stack comes with it automatically, covering firewalls, malware scanning, and DDoS protection. Translation: this blocks common break-in attempts, scans for infections, and absorbs traffic spikes designed to knock a site offline.
  • Version control: every change to the site is tracked, so there’s a history to roll back to if an edit breaks something, or if an unauthorized one gets through.
  • Coderick AI payments: payments here run through Stripe’s hosted page, so card numbers never touch the platform’s underlying code. It’s one of several payment features in Coderick AI built to remove risk before you write a line of setup instructions.
Restore a previous version of project in Coderick AI

This lines up with security research on vibe-coded websites more broadly: build method is exactly why security gaps show up in the first place, which is why having some of it handled by default matters.

Where a developer still needs to check the rest

Coderick AI’s built-in Stripe checkout draws a clear line between what’s handled for you and what isn’t:

  • Handled without a developer: one-time purchases and recurring subscriptions.
  • Still needs a developer: splitting a single payment between multiple parties, a custom pricing engine, or a marketplace where customers shouldn’t see each other’s data.

Every AI website builder draws this same line somewhere, Coderick AI included. Look at code-free checkout options first to see how far you can get without a developer, then bring in one specifically for a paid app flow review once you know what needs custom logic.

Build an AI-built store your customers can trust

Are AI-built online stores safe for real payments once you’ve gone through that list? They sure can be, but only in the past tense, after you’ve actually run it against a live transaction, and not while it’s still sitting on a to-do list. Coderick AI is an AI builder with launch controls already pointed at the specific risks above: built-in authentication, inherited hosting security, version history, and Stripe checkout that never lets card data touch your code.

You’ll still want to run the checklist. Coderick AI just gets you started several items ahead, not at zero. If you’re ready to put a store in front of real customers and real payments, build your trusted AI project and run this same checklist against it before you take your first order.

[96]

Frequently asked questions

Are AI-built online stores safe for real payments?

Yes, AI-built online stores are safe for real payments when you verify checkout, payment status handling, and post-payment confirmation before launch, rather than assuming a finished-looking site is a tested one. The build method doesn’t determine safety. What you checked before your first real transaction does.

What makes an AI-built online store safe to launch?

An AI-built store is safe to launch once it passes eight checks: a clear offer, visible trust signals, upfront policies, minimal data collection, a working checkout, mobile compatibility, accurate payment status handling, and a tested confirmation flow. Skipping any one leaves a gap that only shows up once real money is involved.

Can an AI-built store process payments securely through Stripe?

Yes. An AI-built store can process payments securely through Stripe when Stripe processes the actual payment on its own PCI-compliant infrastructure, so card details never sit on your AI-built store’s servers. What still needs checking on your end is whether your store correctly reflects Stripe’s payment status back to the customer, since a secure processor doesn’t guarantee an accurate confirmation screen.

What should I test on an AI-built store before accepting real payments?

To test an AI-built store before launch, run a full transaction end to end: place a real order, use a card built to simulate a decline, cancel mid-checkout, and request a refund. Then repeat the same order on a phone. If any of those scenarios produces a confusing result for you or the customer, fix it before accepting a real payment from someone who isn’t testing.

What are the risks of using an AI-built online store?

The main AI-built store risks are unreviewed AI-generated content, like a wrong price stated with total confidence, thin post-payment handling with no clear status tracking, and gaps between what the builder covers by default and what still needs a developer, such as custom payment splits. None of these are reasons to avoid AI-built stores. They’re reasons to test one before it takes real money.

Shopify vs. WooCommerce vs. AI-built store: Choose by payments, setup, and control

Abstract of Shopify vs. WooCommerce vs. AI-built store

Searching “Shopify vs WooCommerce” for a business with no warehouse and nothing to ship, just a coaching package, a photography session, or a members-only newsletter, is the first sign you’re comparing the wrong two things. The real question is Shopify vs WooCommerce vs AI-built store, and it isn’t decided by platform popularity. What you’re actually selling decides it first, then payments, setup time, and long-term control decide it from there.

Key takeaways:

  • Shopify vs WooCommerce vs AI-built store comes down to one question: are you selling a product catalog, or something else?
  • An AI-built store skips the product catalog step and can go live with a working payment flow in hours, not weeks.
  • Coderick AI’s Stripe-based checkout accepts real payments for products, services, bookings, digital downloads, and subscriptions.
  • Service businesses, bookings, memberships, and portfolio sites rarely fit the product-catalog assumption behind a typical Shopify vs WooCommerce comparison.
  • If you need full inventory, tax, and multichannel tooling, a full platform earns its complexity. If you don’t, an AI-built selling flow usually gets you to a first sale faster.

Shopify vs. WooCommerce vs. AI-built store: What each option actually solves

Each option solves a different problem before it solves any feature comparison. Here’s what each one is actually built to do.

Shopify: a hosted, retail-ready ecommerce platform

Shopify is a hosted platform built for retail: a product catalog, cart, checkout, and fulfillment tools that work right out of the box. You don’t manage servers or software updates.

  • What’s included: Hosting, security patches, and PCI compliance, all handled inside Shopify’s own admin and theme system.
  • Entry cost: As of August 2026, the Basic plan runs $39 a month, or $29 a month billed annually, plus a 2.9% + 30 cent card transaction fee through Shopify Payments. Adding functionality beyond the core plan typically means paying for separate apps.
  • Next tier: The Grow plan, formerly called the “Shopify” plan in older comparisons, runs $105 a month (as of August 2026) and adds stronger reporting and up to five staff accounts.
  • The trade-off: A retail-ready storefront and predictable support, in exchange for a monthly subscription, a percentage of every sale, and costs that can climb quickly once you’re paying for apps to cover features the core plan doesn’t.

For a business selling 20 or 200 product variants, this level of out-of-the-box functionality is usually worth it. For a business selling one service package or a single paid course, it’s a lot of catalog infrastructure you’ll never use.

Worth knowing
SiteGround Ecommerce is a hosted, all-in-one store builder aimed at the same retail-catalog businesses Shopify serves. Instead of hunting down and paying for a separate app every time you need a new feature, the core pieces come built into the plan itself, running on SiteGround’s own hosting infrastructure for speed and uptime, with SiteGround’s support team behind it if something goes wrong.

WooCommerce: self-hosted control on WordPress

WooCommerce is a free, open-source plugin that turns a self-hosted WordPress site into a store. You own the code, the data, and the hosting account, and nothing about your setup is locked into a vendor’s theme system or app marketplace.

  • Core plugin: Free to install.
  • Real cost: A production-ready store realistically runs $500 to $3,000 a year once hosting, an SSL certificate, a premium theme, and a handful of paid extensions are stacked in, and that’s before a developer touches it.
  • Hosting range: Entry-level hosting often starts around $3 to $15 a month, though renewal rates are commonly higher, and costs climb further as a store’s traffic and resource needs grow.
  • What you get: Full code and data ownership, plus the entire WordPress plugin ecosystem, tens of thousands of extensions covering shipping, tax, subscriptions, and marketing.
  • The trade-off: Full ownership and lower platform costs, in exchange for an ongoing maintenance job and costs that climb as you add plugins to cover missing features. Plugin updates, security patches, and the odd conflict between extensions are yours to handle indefinitely, whether that’s your own time or a developer’s you’re paying for. If you haven’t run a WordPress site before, expect a real learning curve before any of it feels routine.
Adding WooCommerce as a plugin in WordPress

AI-built store: a custom selling flow, not a catalog platform

An AI online store builder isn’t a smaller Shopify or a simpler WooCommerce. It’s a custom online store with AI generating the structure from a plain-language description: tell it what you sell, and it builds the pages, forms, and checkout flow around that.

  • How it’s built: No product-catalog template to start from. The structure, pages, and forms come from your description, not a theme picker.
  • Payments: If you use a platform such as Coderick AI, the payment flow inside an AI build can run through Stripe. That means a generated site can accept cards, Apple Pay, and Google Pay directly.
  • The trade-off: Less catalog and inventory depth than Shopify or WooCommerce, in exchange for a setup that skips platform selection, theme shopping, and plugin configuration almost entirely.
An AI built website created by Coderick AI from a single prompt

Do you need a full ecommerce platform?

The fastest way to know if you need a full ecommerce platform is to count what you’re actually managing, including your catalog of physical products with variants, stock levels, and shipping rules. If that list is short, a full platform is solving problems you don’t have yet. Let’s break it down.

Signs a full platform earns its complexity

  • You stock 20 or more product variants, or manage physical inventory across more than one location.
  • You need multichannel selling: the same catalog listed on your site, a marketplace, and social shops at once.
  • You collect ecommerce sales tax across multiple states or countries and need automated calculation, not a spreadsheet.

If your business matches that list, a full platform, whether that’s Shopify, WooCommerce, or SiteGround Ecommerce is a more realistic starting point than an AI-built selling flow.

When a simple payment flow is enough

A simple payment flow is enough when your business model involves services, bookings, digital downloads, or paid access rather than a shelf of physical products. What you actually need is simply a payment-ready store, and not a complex catalog platform. That means a page that explains what you offer and a checkout that takes the payment. Easy as that.

Getting there without hiring a developer is the whole appeal of an AI-built store. You describe what you sell, and the builder generates a checkout without development and a working payment page without a line of code or an eye-crossing plugin stack to configure.

If your product list is short and stable, this is usually the faster and cheaper path to a first sale.

A website selling only one service with a simple payment flow

Shopify vs. WooCommerce vs. AI-Built Store at a glance

The table below distills payments, setup time, control, cost, and best-fit business type across all three selling setups.

DimensionShopify/ecommerce platformWooCommerceAI-built store (Coderick AI)
PaymentsShopify Payments or third-party gateways; 2.9% + 30 cents standard rateAny gateway via plugin: Stripe, PayPal, WooCommerce PaymentsPayment processor varies by builder; Coderick AI, for example, uses Stripe (and thus Apple Pay, and Google Pay)
Setup timeDays to weeks, including theme and app setupDays to weeks, plus hosting and plugin configurationHours for a basic selling flow
Control and customizationModerate; bound by themes and apps system, or more complex code editingHigh; full code and hosting ownershipLow to moderate; generated structure, limited deep customization
Ongoing maintenanceLow; handles hosting, security patches, and platform updatesHigh; you or a developer handle plugin updates, security patches, and the occasional plugin conflict indefinitelyLow; hosting and platform updates are handled by the builder
Typical annual cost$468 to $4,788+ plus transaction fees and apps$500 to $3,000+ plus developer time if neededSingle subscription; hosting included
Best-fit business typeRetail catalogs, multichannel sellersContent-and-commerce hybrids, custom integrationsServices, bookings, paid access, portfolios

Cost is rarely a single number on any of these three. The store cost tradeoffs above show why the advertised monthly price is only the starting point, not the realistic annual figure, once transaction fees, apps, extensions, or hosting are factored in.

Where Shopify and WooCommerce pull ahead of an AI-built store

The evidence here favors a full platform once a catalog gets complex enough to need real inventory and integration tooling.

Shopify vs. AI-built store: catalog, inventory, and multichannel selling

Shopify vs an AI-built store is a clear win for Shopify (or other competent ecommerce website builders) once your catalog crosses a few dozen SKUs. These are core ecommerce website builder features, not add-ons:

  • Built-in inventory tracking across multiple locations.
  • Product variants, such as size, color, and material, managed natively.
  • Native listings on sales channels such as Instagram, TikTok Shop, and Amazon, though the exact channel list varies by platform.

An AI-built store can generate a product page and working payment setup basics in an afternoon. It doesn’t come with inventory management as a built-in feature the way Shopify does, so stock tracking would have to be custom-described and built into the app itself, and keeping that in sync with a separate sales channel, a marketplace or an in-person POS, isn’t something an AI-built store can typically support. For a boutique with 200 SKUs across three sales channels, that gap will matter more than setup speed.

WooCommerce vs. AI-built store: content control and developer flexibility

WooCommerce vs an AI-built store comes down to ownership. WooCommerce gives you:

  • Full code access.
  • A WordPress content system built for long-form blogging and ecommerce SEO.
  • Access to tens of thousands of WordPress plugins, so almost any custom workflow, from a loyalty program to a booking calendar, can be built or bought (although often with added cost).
  • Straightforward payment data in your workflow: syncing orders into a CRM, an accounting tool, or a custom reporting dashboard.

That last one is harder to replicate on a generated AI build that isn’t designed for deep third-party integrations yet. If your business depends on content marketing alongside selling, or on a specific integration WooCommerce already supports, that flexibility is hard to give up.

Where an AI-built store pulls ahead of Shopify and WooCommerce

The evidence runs the other way for service-based, appointment-based, and access-based businesses, where a product catalog was never really the point.

Building an AI-built selling flow instead of a full store

Building an AI-built selling flow instead of a full store starts with a conversation and not a template picker. You describe what you’re selling and who buys it, and an AI builder for selling flows, such as Coderick AI, turns that into a custom selling flow: the pages, forms, and Stripe-based checkout built around your description. This means:

  • No theme to install.
  • No plugin stack to configure.
  • No separate hosting account: the site publishes on the builder’s own hosting the moment you’re ready.
  • Setup typically runs hours instead of the days or weeks a Shopify or WooCommerce launch usually takes once you count theme customization and app setup.

Before sending real customers to it, a short list of AI store launch checks, testing the checkout, confirming pricing and policies display correctly, and checking the mobile view, is worth running through.

For businesses that need more than a page and a checkout, such as a custom ecommerce app with account logins, saved orders, and a dashboard, the same plain-language approach applies: describe the added functionality, and it gets built into the generated site.

Creating an online store website with Coderick AI with a simple prompt

Selling services or taking paid bookings online without a product catalog

Selling services or taking paid bookings online doesn’t require a product catalog at all. It requires:

  • A page that explains the service.
  • A calendar or intake form.
  • A checkout.

An AI-built store can generate all three from a description of the service and the price. This is also where freelancers and small agencies benefit most: handling client selling projects, invoices, and one-off packages inside a generated selling flow skips the overhead of running a full store just to bill a handful of clients a month.

Choosing a platform for paid access, memberships, or gated content

The right choice here comes down to whether you need a member login and drip content, or a full store built around it.

  • Coderick AI can build a members-only area with sign-up, login, and gated pages.
  • A Stripe subscription handles the recurring charge itself.

For a creator or coach selling one membership tier, that’s a recurring revenue setup without a shopping cart, a product catalog, or checkout steps built for buying multiple physical items at once.

Running a portfolio, restaurant, or event-based business

Running a portfolio, restaurant, or event-based business rarely means managing SKUs:

  • A restaurant needs online ordering or reservations.
  • A photographer needs a booking calendar and a way to collect a deposit or shoot payment.
  • An event organizer needs ticket sales tied to a date, not a warehouse.

These are businesses built to sell without a product catalog, and an AI-built store, with Stripe handling the ticket or order payment, matches that shape more closely than a platform designed around stock-keeping units and shipping zones.

How to choose the right selling setup for a small business

Which selling setup is best for a small business depends on one thing first: what you’re actually selling, not which platform has the most reviews.

Start with your business model, not the platform

Start with your business model, not the platform name. Ask what you’re actually selling before you compare features: a product catalog points toward Shopify, WooCommerce (or other ecommerce platforms such as SiteGround Ecommerce), while services, bookings, or paid access point toward an AI-built store or a simple payment flow.

Weigh setup time against long-term control

Setup speed and long-term control rarely move together across these three options:

  • AI-built store: Live fastest, but the structure is generated from your description. A major redesign later usually means describing it again, not editing existing code.
  • WooCommerce: The most control and the most maintenance. Because the code is yours, you can move hosts or rebuild the front end later without starting over.
  • Shopify and similar hosted platforms, such as SiteGround Ecommerce: Sit in between, a subscription in exchange for less upkeep.

Plan for where you’ll need to grow

Think about how you’ll grow, and not just where you’re starting. If you’re not selling yet, or you’re not sure you’ll ever need a full product catalog, an AI-built selling flow gets you live and taking payments now instead of spending weeks setting up a platform you might not need. 

And if that product line does happen? Moving to Shopify or WooCommerce later means rebuilding there rather than exporting and continuing, which is a reasonable trade for the months you spent selling instead of waiting. A business that already knows it needs multichannel inventory can skip that step and start on the full platform directly.

If you’re selling…Start with…
A physical product catalog with 20+ SKUsAn ecommerce platform like Shopify, WooCommerce or SiteGround
A smaller catalog, with full code ownership as a priorityWooCommerce
Services, bookings, or a single paid courseAn AI-built store
Paid access, memberships, or gated contentAn AI-built store with a Stripe subscription
A portfolio, restaurant, or event-based businessAn AI-built store

Where Coderick AI fits compared to Shopify and WooCommerce

Coderick AI is built for exactly the businesses this article has been describing: services, bookings, memberships, portfolios, and short product lists that don’t need multichannel inventory or tax automation across a dozen jurisdictions. Instead of picking a theme and configuring plugins, you describe what you’re selling in plain language, and Coderick AI builds the pages, forms, and checkout around it, then keeps building as the business needs more: a booking calendar, a client portal, an invoice tracker, or an internal dashboard, all as part of the same project rather than a separate app or plugin.

It isn’t positioned as a Shopify or WooCommerce replacement for a retail catalog business; it’s a separate path for businesses that were never trying to run one.

  • How it works: Describe what you’re selling, connect a Stripe account, and Coderick AI generates the pages, forms, and checkout around that description.
  • What’s handled for you: Every project starts on a SiteGround-provided domain and publishes immediately on SiteGround’s own hosting, included in the plan, no separate hosting account to arrange. Connecting your own domain later, with SSL enabled automatically once it’s pointed, is a setting inside your account rather than a separate technical project, backed by the same support team behind SiteGround’s other hosting and ecommerce products.
  • Beyond the storefront: The same prompt-based approach can add a client portal, an invoice tracker, or an internal dashboard to the same project, not just the pages that take payment.
  • Checkout: The Coderick AI checkout setup runs on Stripe, taking cards, Apple Pay, and Google Pay for products, services, bookings, digital downloads, and subscriptions. Running through app checkout readiness, confirming the Stripe connection, testing a real charge, and checking the confirmation flow, takes a few minutes before sending customers to it.
Coderick AI SiteGrounds AI-powered platform in action creating an app

Choosing Shopify vs. WooCommerce vs. AI-built store decision comes down to fit

The right choice here was never about finding the best-reviewed platform. It comes down to naming what you’re actually selling before comparing a single feature, then letting that answer point you to Shopify, WooCommerce, or an AI-built store.

If that’s services, bookings, paid access, or a portfolio without a warehouse behind it, Coderick AI is built for exactly that path. Describe what you’re selling in plain language, and it generates the pages, forms, and Stripe-based checkout around it, with hosting and your domain already sorted. It keeps building as the business grows, too, into a client portal, an invoice tracker, or an internal dashboard, not just a bigger storefront. Create a selling flow with Coderick AI and go from a description to a working checkout in just hours.

[96]

Frequently asked questions

Should I use Shopify, WooCommerce, or an AI-built store?

Use Shopify or WooCommerce if you’re selling a physical product catalog with multiple SKUs, variants, or inventory across channels. Use an AI-built store, such as one built with Coderick AI, if you’re selling services, bookings, digital downloads, or paid access and want a working payment flow without managing a full ecommerce platform.

What’s the difference between Shopify, WooCommerce, and an AI-built store?

Shopify is a hosted, subscription-based platform built for retail catalogs. WooCommerce is a free, self-hosted plugin that turns WordPress into a store you fully control. An AI-built store generates a custom selling flow from a plain-language description instead of starting from a catalog template.

When should I choose Shopify over WooCommerce or an AI-built store?

Choose an ecommerce platform like Shopify or SiteGround when you want a hosted platform with built-in support, predictable updates, and native multichannel selling, and you’re willing to pay a monthly subscription plus transaction fees for that convenience.

When is an AI-built store enough to start selling online?

An AI-built store is enough when you need a payment-ready store for services, bookings, digital downloads, or paid access rather than a physical product catalog, and you want to accept payments without configuring a full ecommerce platform first.

Do I need a full ecommerce platform to sell online?

No. You need a full ecommerce platform only if you’re managing a product catalog with inventory, shipping, and tax across multiple channels. Services, bookings, and paid access can run on a simpler payment flow instead.

Can I sell online with a simple AI-built payment flow?

Yes. Platforms like Coderick AI can often connect to Stripe, so a generated site can accept cards, Apple Pay, and Google Pay for products, services, bookings, digital downloads, and subscriptions.

Is Shopify better for retail stores than AI-built stores?

Yes, for retail stores with a real product catalog. Ecommerce platform inventory tracking, product variants, and native multichannel listings handle catalog complexity that an AI-built store isn’t designed to manage at scale.

When is Coderick AI a better fit than Shopify or WooCommerce?

Coderick AI fits better when you’re selling services, bookings, memberships, or a short list of offerings rather than a full product catalog, and you want a working payment flow without configuring a separate ecommerce platform.

Can Coderick AI help me build a custom selling flow?

Yes, Coderick AI can help you build a custom selling flow. Describe what you’re selling and Coderick AI generates the pages, forms, and Stripe-based checkout around that description, without a theme, plugin, or template to configure first.

What should I compare before choosing an online store builder?

Compare what you’re actually selling, how much setup time you can spend before your first sale, how much control you want over code and hosting, and the realistic annual cost, not just the advertised monthly price, of each option.

Stripe CRM integration: Start accepting payments in the CRM app you already built

A digital graphic depicting payment integration and e-commerce analytics against a dark blue background. In the upper center, a floating white prompt box displays the text "Add a way for clients to pay.." next to a blue arrow action button. Below, a translucent glassmorphism dashboard shows "Monthly Shop Performance" metrics—including "Total Sales" of "USD 423.60," "Avg. Order Value" of "USD 117.67," and "Total Orders" of "24"—sitting above a "Most Recent Orders" table with highlighted order statuses like "COMPLETED." Floating on the right are payment UI elements, including a credit card icon with a green checkmark, alongside "PAID" and "UNPAID" status badges.

If you’ve already built your CRM app, payments are probably the piece you left for later. And no wonder: taking card details yourself makes you responsible for storing them safely, so you’ll probably want to hand that job to a payment provider your customers already recognize. For many CRM apps, that means integrating Stripe, one of the most trusted and widely used payment providers in the world.

Stripe CRM integration connects Stripe payments back to your customer records, so you can collect money from the same place you already track customers, and the payment status appears against the right person. It works two ways: connect Stripe to an off-the-shelf CRM, or build the payment flow into an app you own.

Key takeaways:

  • Stripe CRM integration puts payment status on the customer record. Instead of checking two systems, you see who has paid, what they bought, and what should happen next, in the place you already work.
  • Building it no longer means writing code. With an AI app builder such as Coderick AI you describe the payment behavior you want and it builds the checkout, then connects your own Stripe account.
  • The webhook is the source of truth, not the thank-you page. Stripe sends your app a separate message when a payment actually completes. Never record a payment based on the customer landing back on your site.
  • Granting access is only half the job. Refunds, disputes, and cancellations need handling too, or a refunded customer stays marked paid and keeps access indefinitely.
  • Test the whole thing before real money moves. Stripe’s test mode lets you run every path, including a card that deliberately fails, without charging anyone.

What Stripe CRM integration means

CRM payment integration means payment activity and customer records stay connected in the same system, so nobody reconciles a spreadsheet of payouts against a list of customers by hand. CRM payment processing can reach that point two ways, and which applies to you depends on where your customer data sits today.

RouteWhen it is the right answerWhat it involves
Connect Stripe to an off-the-shelf CRMYou already pay for a CRM that ships a Stripe connector, or supports one through an automation toolAuthorizing the connector and mapping fields
Build the payment flow into the app you already haveYou built your own CRM or app, your CRM has no connector, or the payment step needs to sit inside a workflow your CRM does not modelAdding a checkout step and a way for your app to record what Stripe confirms

Connecting Stripe to an existing CRM

If you already pay for a CRM that offers a Stripe connector, use it. Most major CRMs either ship one or reach Stripe through an automation tool, and setup is usually authorizing the connection and choosing which events update which fields.

Check two things first: what the connector actually syncs, since some bring across payments but not refunds or failed renewals, and whether it can trigger the workflow you care about rather than just showing a payment history.

Pro tip: Read the connector’s fine print before you rely on it. “Stripe integration” on a CRM pricing page can mean a live two-way connection, a one-way import of past payments, or just a link out to your Stripe dashboard. Only the first keeps a record current. Ask the vendor two questions before committing: does it write a refund back to the record, and can a payment trigger something, such as moving a stage or sending an email. If either answer is no, you will still be joining things up by hand.


Adding Stripe payments to the CRM app you already have

If you built the app yourself, there’s no connector to install. You’re not rebuilding anything. You’re adding a Stripe checkout step for the customer, and a way for your app to hear back from Stripe and update the right record. You can also add Stripe payments to Coderick AI projects, which puts that within reach without writing code.

This is also where an AI app builder for business workflows changes the practical difficulty, because the work is mostly wiring rather than something creating, and wiring is something you can easily describe in a sentence.

What has to happen in your CRM when a customer pays

It helps to understand the whole sequence:

  • Your app sends the customer to Stripe. They click a pay button on a customer record, an invoice, or a booking page.
  • Stripe collects the payment on its own page. Card details go to Stripe and never touch your app or its code, which is why you are not responsible for storing them.
  • Stripe sends your app a message confirming what happened. This message is called a webhook: your app has a URL that sits waiting, and Stripe posts an event to it when a payment succeeds, fails, or is refunded.
  • Your app updates the customer record. It matches the event to the right customer, marks them paid, records what they bought, and stores the Stripe reference.
  • The customer comes back to your app. They land on a confirmation page. This happens in parallel with the webhook and is not the same thing.

The customer’s return trip and Stripe’s message to your app are separate events. A customer can close the tab before returning and the payment still happened. Someone can reach your confirmation page without paying at all. Trust the webhook; the redirect exists so the customer sees something friendly.

There are two ways to take the payment, and the difference is how much of the flow lives inside your app.

A Stripe payment link is a hosted checkout page with its own URL, created in your Stripe dashboard or generated for you, with nothing to build. You can email it, put it on a booking confirmation, or store it against a customer record and send it when a job is done. Using Stripe payment links in CRM workflows is the quickest way to accept payments in CRM software you already run, and for many service businesses it is enough on its own.

The limit is that a bare payment link doesnчt know who clicked it. To have a payment land against the right record automatically, you pass an identifier through the link so the webhook can match it back, which is where the second option usually wins.

Stripe Checkout: when the payment sits inside the app

Stripe Checkout for CRM means your app creates the checkout at the moment the customer clicks and attaches your own identifiers, such as the customer ID and the job ID. Stripe still hosts the payment page, so card handling is unchanged, but the event that comes back carries those identifiers and the record updates itself.

Start with a payment link if you want money moving this week. Move to Checkout when you want the payment status to appear on the right record without anyone copying anything across.

How to add a payment flow with Coderick AI

If you build your CRM app with Coderick AI, you can add Stripe payments by describing the payment behavior you want in the chat and it builds the flow, including the products, the checkout, and the confirmation page.

A specific prompt is more useful than “add payments.” You can name the record, the trigger, and what should change afterward. Something closer to this:

“Add Stripe payments to my app so I can collect payment on a sale. Add a ‘Collect payment’ button on each sale that opens Stripe Checkout for the sale’s value, and mark the transaction as paid once the payment succeeds.“

Here’s an example of what Coderick AI gives you after this prompt: an option to integrate Stripe right in the chat.

A screenshot of the SiteGround Coderick AI web development interface showing a split view with an AI assistant on the left and a live application preview on the right. The left panel features an AI response regarding Stripe payment setup, a Stripe integration prompt with a "CONNECT" button, a credit usage alert, and a prompt input asking "What do we build next?" The right panel displays a preview of a web application titled "Ledger SALES DESK," showcasing a dark panel with the headline "Every lead, deal, and follow-up on one desk." beside a login form featuring email and password fields, a dark "Sign in" button, and a "Create an account" link.

The Collect payment button, the hand-off to Stripe, and the confirmation page are all ready; your Stripe key is what’s missing, so the chat says so plainly and shows a Connect card underneath. Click Connect and a dialog asks for your Restricted Key, which you copy from your own Stripe account. It goes in that dialog, never into the chat. A checkpoint is saved at the same moment, so you can preview what was built or roll back to it if the next change goes wrong.

Coderick AI connects to Stripe using a Restricted Key rather than your main secret key, so you choose exactly which permissions to grant, and a key beginning rk_test keeps you in test mode until you swap in rk_live. And the key goes into the connection dialog, never into the chat itself. The full setup guide covers creating the key and what each permission does.

What this doesn’t do is remove your responsibility to understand the flow. The builder handles the wiring. You still decide what happens after a refund, who can see paid features, and what the record should say.

Six CRM payment-flow mistakes that break payment status

These are the failures that cost real money, and they are the reason a payment flow can look finished while being wrong. Each one is worth checking whether you built the flow yourself, had it built, or described it to an AI builder.

What goes wrongWhat the business actually seesWhat to do instead
Duplicate webhook eventsStripe occasionally retries an event. A naive database insert records one payment twice, so two paid orders exist for one payment and CRM revenue stops matching StripeCheck whether the Stripe event ID has already been processed before acting, or make the write an update keyed on the Stripe object ID so repeats overwrite rather than duplicate
No revocation pathOnly the payment-succeeded event is handled. After a refund, a chargeback, or a failed renewal, the record stays marked paid and the customer keeps access indefinitelyHandle refund, dispute, and cancellation events too. Granting access is half the job; removing it is the half that gets forgotten
Access checked only in the browserA customer edits JavaScript in their own browser and reaches paid features without payingEnforce every paid-feature check on the server, not in frontend code
Trusting the success redirect instead of the webhookA customer closes the tab after paying and is never recorded as paid. Or the success page is reached without any payment completingTreat the webhook as the source of truth for payment state. The redirect is for the customer’s experience, not for your records
Secret key exposedThe Stripe secret key ends up in frontend code or committed to a repository, where anyone who finds it can use it against your accountKeep secret keys server-side only, never in frontend code and never committed. Prefer a restricted key scoped to just the permissions the integration needs
No webhook signature verificationA forged request marks orders as paid without any money movingVerify the webhook signing secret on every incoming event before processing it

These six mistakes cost money in more ways than the missed sale. Stripe keeps its processing fee when you refund a payment and charges a separate fee for every dispute, so a refunded customer who keeps access costs you the sale, the fee, and whatever you go on delivering to them. Factor those payment gateway fees into your prices before launch. None of this is specific to Stripe either. PayPal, Square, and most other providers also confirm payments through webhooks, retry failed deliveries, and sign their events, so the same six checks apply whichever provider you use to add payments to an AI-built app.

If the payment worked but the record didn’t update, Stripe will tell you why. Your Stripe dashboard logs every event it tried to send your app, whether your app answered, and what it said back. That log separates three very different problems: Stripe never sent the event, Stripe sent it and your app never answered, or your app answered with an error. Without it you are guessing which half of the flow is broken.

How to test before you take real money

Stripe gives you a complete test environment, so you can be wrong for free. Run all of this before a real card is involved.

  • Connect in test mode first. Keys beginning rk_test or sk_test cannot move real money, so nothing you do here can charge anyone.
  • Pay with Stripe’s test cards. Stripe publishes card numbers that always succeed, so you can complete the entire flow yourself and watch the record update.
  • Run the declined-card path deliberately. Stripe also publishes cards that always fail. Use one, and check that your app does not mark anyone paid.
  • Close the tab immediately after paying. This is the test almost nobody runs, and it is the one that catches a flow relying on the redirect. If the record still updates, your webhook is doing its job.
  • Refund the test payment in your Stripe dashboard. Then check whether the customer record went back to unpaid and whether access was removed. If it did not, you have found the revocation gap before a real customer did.

Only once all five behave correctly should you swap in your live key. On Coderick AI, that means replacing the test key from the Integrations menu, and the test to live mode guide covers the switch.

Test mode and live mode are separate worlds, and nothing crosses over. Products, prices, customers, and payment links created in test mode do not exist in live mode, and neither do your webhook settings. So the first live payment is not the test flow with real money in it, and a flow that worked on Friday can fail on Monday because what it pointed at was never created on the live side. After switching keys, run one small real payment to yourself and refund it before sending anything to a customer.

What payment status in your CRM should show after someone pays

This is what justifies having a CRM rather than just a checkout. A payment is a fact about a customer that should change what happens next.

At minimum, the customer payment status should distinguish four states rather than a single paid checkbox: unpaid, paid, refunded, and failed or overdue. A checkbox cannot represent someone who paid and was then refunded, which is the case that causes trouble later.

Alongside the status, store what they bought, the amount, the date, and the Stripe reference, so any record traces back to the transaction in your Stripe dashboard. Stripe stays the system of record for the money, and your app holds what the money means.

Then let the status do some work. Paid can trigger the onboarding email, move the deal stage, or schedule the booking. Overdue surfaces the record in a follow-up list. Refunded revokes access and flags the account. Tracking paid and unpaid customers in a CRM only pays off when the status changes something automatically, which is the reason to put payments where the customer data already lives.

Stripe handles the money, your app handles the meaning

Stripe CRM integration is easier to reason about once the division of labor is clear. Stripe takes the card, checks it, moves the money, and keeps the authoritative record of every transaction. Your app decides what that payment means for the customer: what they now have access to, what stage they are at, and what should happen next.

Almost everything that goes wrong is the second half falling out of step with the first. The payment succeeds and the record does not update, or the refund goes through and the access stays on. Build the checkout, then spend your remaining effort on the states, the revocation path, and the tests above.

[96]

FAQs

What is Stripe CRM integration?

Stripe CRM integration connects Stripe payment activity to CRM customer records, so payments can be collected from the same workflow where you already track customers and the resulting payment status appears against the right record. It can mean connecting Stripe to an off-the-shelf CRM, or building the payment flow into an app you own.

How do I add Stripe payments to a CRM?

To add Stripe payments to a CRM, either enable your CRM’s Stripe connector, or add a checkout step and a webhook handler to an app you built. The connector route is faster when it exists. The build route is what you use when the CRM is your own.

Can I connect Stripe to a CRM app I already built?

Yes. You can connect Stripe to a CRM app you already built without rebuilding it. You add a checkout step for the customer and a webhook handler that updates the customer record when Stripe confirms the payment.

Can a CRM track Stripe payment status?

Yes. A CRM can track Stripe payment status when your app listens for Stripe webhook events and writes the result to the customer record. The webhook, not the browser redirect, is what tells you a payment actually completed.

How do I connect Stripe payments to customer records?

To connect Stripe payments to customer records, pass an identifier such as the customer ID through the checkout session, then read it back from the Stripe event and update the matching record. Without that identifier, a payment arrives with no reliable way to tell whose it was.

Can Coderick AI build a CRM that accepts Stripe payments?

Yes. Coderick AI can build an AI-built CRM with Stripe payments. You describe the payment behavior you want in the chat, connect your Stripe account with a restricted key, and it builds the checkout, the products, and the confirmation flow around your existing records.

Can I use Stripe Payment Links inside a CRM workflow?

Yes. To use Stripe payment links inside a CRM workflow, store a link against a customer or job and send it when payment is due. To have payments land against the right record automatically, pass an identifier through the link or use Stripe Checkout instead.

How do I track paid and unpaid customers in a CRM?

To track paid and unpaid customers in a CRM, store a payment status on each record that covers unpaid, paid, refunded, and overdue, updated from Stripe webhook events rather than entered by hand.

What should happen in a CRM after a customer pays through Stripe?

After a customer pays through Stripe, the CRM should mark the record paid, store what they bought and the Stripe reference, and trigger whatever comes next, such as granting access, moving the deal stage, or sending onboarding. It should also be able to reverse all of that if the payment is later refunded.

WordPress security maintenance with AI: A safer routine for small business sites

A digital graphic illustrating AI-powered WordPress security and maintenance against a blue gradient background. On the right, a smiling man in an olive green sweater works on a laptop. In the background, a dark WordPress dashboard features a green badge reading "Website secured" with a shield check icon. In the foreground, a floating translucent UI card displays the user prompt "Review my plugins and users..." next to his avatar, followed by an AI status reading "Reviewing..." alongside a SiteGround logo, with a white sparkle symbol floating nearby.

WordPress security maintenance is the recurring work of keeping your site’s exposure small: updating WordPress itself along with your plugins and themes, checking what’s installed, reviewing who has access to the dashboard, removing what you no longer use, and confirming your backups ran. It’s basic housekeeping, and it’s separate from the tools that guard your site, but it’s just as important.

And for small business owners who manage their own WordPress websites, it’s another nuisance to think about. Our 2026 report on AI in WordPress for small businesses found that 67% of small business owners run their site entirely themselves, with no agency or freelancer behind them, and 28.9% named security and updates among the things they find hardest. What many don’t know is that an AI assistant can now help with WordPress security maintenance by connecting to their site and carrying out recurring tasks through a simple chat.

Key takeaways:

  • Protection and WordPress security maintenance are two different jobs. Protection is your firewall, malware scanner, and host, running around the clock. Maintenance is updates, audits, and access reviews, and it basically depends on you.
  • Most small business owners handle WordPress security maintenance alone. 67% of small business owners manage their site entirely themselves, and 28.9% find security and updates among the hardest parts, as per SiteGround’s report.
  • A specialized AI assistant like SiteGround’s AI Agent for WordPress can help you complete WordPress security maintenance faster and more consistently. It can do things like update plugins and themes, check what’s installed, and review users and roles.
  • You shouldn’t postpone your WordPress security maintenance work for too long. It takes five hours between a flaw being made public and the first attack on it.

What WordPress security maintenance actually covers

Most writing on this subject blurs two things that need to stay apart: the tools that watch your site continuously, and the housekeeping that keeps its exposure minimal. They work at different levels (and can fail in different ways):

LayerWhat it coversWho or what does it
Security protectionFirewall, malware scanning, watching for newly announced weaknesses, login protection, server hardening, cleanup after a break-in, and the backup system itselfDedicated security plugins, your host, or a managed service.
Security maintenanceUpdates to WordPress, plugins, and themes; checking what is installed; reviewing who has access; removing what you do not use; checking settings; and doing it again next monthYou. An AI Agent can help you complete much of this faster and more consistently.
The overlapBackups. The system that takes them is protection, but confirming they ran and knowing how to restore is maintenanceYour host or backup tool provides it. You confirm it, with or without AI help.

Security protection: what your tools and host do

Protection runs whether or not you are paying attention:

  • A firewall sits in front of your site and checks incoming visitors before they reach it, turning away requests that match known attack patterns. You may see it called a WAF, short for web application firewall.
  • A malware scanner reads through your site’s files looking for malicious code, which is code an attacker has added to make your site do something you did not intend, such as redirecting your visitors to another site.
  • Vulnerability monitoring watches for public announcements that something you have installed has a newly discovered weakness. A vulnerability is a flaw in a piece of software that someone can misuse to get in.
  • Login protection blocks repeated password guessing, known as a brute-force attack, where software tries thousands of passwords until one works.
  • Server hardening is your hosting company tightening the settings on the machine your site runs on, so that even a successful attack has less room to move.

None of this is a daily task for you. It runs continuously and automatically, which is why it belongs to dedicated security plugins and your hosting provider.

Security maintenance: what stays your job

While security protection runs automatically, security maintenance is something that gets done, over and over, and it involves judgments about your particular site: which plugins you actually still need, who should be able to log in, what is safe to remove. That is why it stays with you even when you have good security tools running.

Four things can help explain why these tasks matter more than they look:

  • An update is a fix you have to install. When a plugin developer finds a security flaw, they fix it and release a new version. Until you install that version, your site is still running the flawed code, and by then the flaw is public knowledge. The fix existing does nothing for you. Installing it does.
  • Access only ever accumulates. Everyone who has ever needed to log in still can, unless somebody removes them. Most people get given the administrator role, the highest level of access in WordPress, because it is the fastest way to unblock someone. A WordPress user access audit is going through that list and asking who still needs to be on it.
  • An abandoned plugin looks exactly like a maintained one. Nothing in your dashboard turns red when a developer stops working on a plugin. It stops receiving updates and carries on running as before. The only way to find out is to look.
  • A backup you have never restored is unproven. Backups fail without announcing it. A setting changes, a disk fills up, a plugin interrupts the process, and the report still says the job completed. You find out whether the backup is any good at the moment you need it most.

None of these tasks is difficult, which is what makes them easy to put off. There’s no deadline, nothing visibly breaks, and skipping them appears to cost nothing. Except when it does.

Why postponing WordPress security maintenance is riskier than it used to be

Two things changed recently, and neither is about WordPress itself getting worse. The first is volume: Patchstack’s annual security report recorded 11,334 new weaknesses across WordPress plugins, themes, and WordPress itself in 2025, 42% more than the year before and roughly 200 a week. The second matters more: the dangerous share grew faster than the total. Highly exploitable flaws rose 113% in a single year, and more high-severity ones were found in 2025 than in the previous two years combined. The same monthly check now covers more ground, and more of what it covers is worth attacking.

Where those weaknesses live has not changed. 91% were in plugins, and siix were in WordPress itself, all low priority. This basically means WordPress plugin security is a big part of the problem.

About half of high-impact weaknesses are attacked within 24 hours of becoming public, and weighted by how heavily each one was targeted, the median gap between a flaw being announced and the first attack on it was five hours.

No maintenance routine closes a five-hour gap. Nobody checks their site every five hours, and 46% of flaws had no fix available from the developer when they were disclosed, so updating sooner would not have helped in almost half of cases either. That’s the argument for dedicated protection running underneath your routine.

What a routine does fix is the backlog. Every skipped week adds unpatched plugins, unreviewed accounts, and code you have forgotten is still there. Plugins are sometimes pulled from the WordPress directory over security problems that never get fixed, and if one of yours has been pulled, updating will never help.

The recurring WordPress security maintenance checklist

Six tasks make up a WordPress security checklist within any broader WordPress maintenance checklist. None is complicated on its own. The value comes from doing them regularly instead of when something goes wrong.

TaskWhat it preventsHow often
Update WordPress, plugins, and themesPublished weaknesses being used against you when a fix already existsWeekly, and straight away for anything under active attack
Check what is installedAbandoned or withdrawn plugins sitting on your site unnoticedMonthly
Run a WordPress user access auditOld accounts and contractors who still have full administrator accessMonthly
Delete plugins and themes you don’t useInactive code that can still be attacked and still needs patchingQuarterly
Confirm backups ranFinding out during an emergency that the backup you counted on was never being takenWeekly
Check your settingsOptions that were changed for a one-off reason and never changed backQuarterly

Deleting unused WordPress plugins and themes is the task many people skip, because switching a plugin off feels like enough. However, deactivated code still sits on your server, can still be reachable, and still needs patches that nobody is applying because you stopped thinking about it. Switching off is a pause, while deleting is the fix.

Where an AI Agent helps with WordPress security maintenance

A specialized AI assistant like SiteGround’s AI Agent for WordPress is connected directly to your site, so that instead of only answering questions, it can make actual changes in your dashboard when you ask. For instance, if you ask a chatbot like ChatGPT in another browser tab how to update your plugins, it will explain the steps. But if you ask an AI connected agent, it can actually update them for you.

What an AI Agent can help you complete

Every task in the checklist above is something you would otherwise do by clicking through the dashboard, which means it is something the AI Agent for WordPress can do on request:

  • Updating WordPress core, plugins, and themes, individually or in bulk, with approval for higher-risk changes.
  • Managing plugins and themes across their lifecycle: listing what is installed, explaining what each item appears to do, activating, deactivating, updating, or removing unwanted items after approval.
  • Pointing out plugins or themes that look inactive, redundant, outdated, abandoned, or suspicious, so the quarterly clear-out becomes a short list to review rather than a full investigation.
  • Reviewing and managing users and roles, from listing administrator accounts to creating users, updating profiles, changing roles, downgrading access, or removing accounts after approval and content reassignment.
  • Helping configure WordPress-level or compatible plugin-level security settings, such as login protection or hardening options, when those controls are available inside the site.
  • Repeating the same routine across multiple connected sites, instead of opening one dashboard after another.

Here’s an example prompt you can give to the AI Agent for WordPress:

“Run a WordPress security maintenance review: core, plugins, themes, users, roles, comments, and supported security settings; identify updates, risky or inactive items, admin accounts, and cleanup tasks; group everything by risk; then ask for approval before making changes.”

The AI Agent sorts what it finds into high, medium, and low risk, lists the plugins, themes, users, and settings it checked, then proposes a specific plan: deactivate this, delete those two, switch on these three settings, leave the rest alone.

A screenshot of the AI Agent by SiteGround interface displaying a Recommended cleanup plan for a WordPress website. The outlined plan categorizes tasks including deactivating the WordPress Beta Tester plugin, deleting inactive themes (Twenty Twenty-Four and Twenty Twenty-Three) while retaining Twenty Twenty-Five, enabling security settings like two-factor authentication, and noting an optional decision for inactive Akismet. At the bottom sits a text input box with the placeholder "Ask me anything WordPress related and I'll help."

Approve the plan and it works through it, then reports back on what it changed. Anything it was not sure about it leaves alone and asks about separately, so any genuine judgment calls come back to you.

A screenshot of the AI Agent by SiteGround chat interface following up on site cleanup tasks. At the top right, a user prompt reads "Proceed with the recommended changes." In response, the "WordPress Expert" assistant confirms that the approved recommendations have been completed—listing the deactivation of the WordPress Beta Tester plugin, deletion of Twenty Twenty-Four and Twenty Twenty-Three themes, enablement of two-factor authentication and readme file removal, and disabling of default pingbacks. The assistant then asks whether to delete Akismet or keep it installed for future anti-spam configuration. At the bottom, an input box sits with the placeholder "Ask me anything WordPress related and I'll help."

For more prompts you can reuse and adapt, read our guide on how to turn WordPress admin work into simple conversations.

What an AI Agent cannot do for WordPress security

An AI Agent doesn’t run a firewall, and it doesn’t scan your files for malware. It doesn’t watch vulnerability announcements overnight and wake up when something you have installed comes under attack. It doesn’t itself block password-guessing attempts in real time, although it may help configure a security tool that does. It doesn’t harden the server itself, although it may help adjust WordPress-level hardening settings.

The reason is structural rather than a gap somebody will close in the next version. An agent acts when you ask it to, working through the same WordPress controls you would use yourself.

A firewall works somewhere else entirely: it inspects every request arriving at your site, thousands of times a day, before WordPress even starts loading. A malware scanner reads every file on a fixed schedule. Vulnerability monitoring watches disclosure feeds around the clock and does not wait to be asked. Those jobs are continuous, automatic, and positioned underneath or in front of the layer an assistant works in.

How to run AI-assisted WordPress security updates without breaking your site

Applying WordPress security updates quickly matters, especially when an update fixes a security issue. But updating carelessly creates its own problems. An AI Agent can reduce the manual work, organize the process, and add approval steps before high-impact changes, but it cannot make live updates risk-free. A plugin, theme, or WordPress core update can still introduce a bug, conflict with another extension, break checkout, alter layouts, or trigger a compatibility issue.

The safest way to use AI is not to let it push every update blindly. It’s to use it as an operator with guardrails: inventory first, plan the work, update in controlled batches, and keep a rollback path ready.

  • Back up before you update, and know how to restore. A backup you have never tested is a hope rather than a plan. The AI Agent can help coordinate the update routine, but it is not the backup or restore system, so the restore point needs to exist before changes begin.
  • Test complicated or business-critical updates on a staging copy first. WooCommerce, payment plugins, page builders, membership plugins, booking systems, multilingual plugins, caching tools, and major theme updates can break important parts of a site. The AI Agent can help identify which updates belong in the staging-first group before anything touches the live site.
  • Use AI to plan and batch the work, not to remove judgment. Instead of updating everything at once, ask the agent to list available updates, group them by risk, and run smaller batches. If something breaks after one giant update batch, it is much harder to know what caused it.
  • Keep approval over anything with a large blast radius. Deleting plugins, removing themes, changing user roles, modifying security settings, and running bulk operations should pause for confirmation. A good AI-assisted workflow keeps the agent as an operator, not an unchecked autopilot.
  • Check the site after meaningful update batches. Visit key pages, test forms, confirm the dashboard is not showing new errors, and run through checkout if you sell online. The AI Agent can report which updates completed successfully, but it cannot replace checking the real user journeys your site depends on.
  • Know how to undo an update before you need to. For posts and pages, WordPress revisions may help. For plugin, theme, core, or database-impacting changes, your real rollback plan is usually a backup, restore point, staging copy, or dedicated rollback tool.

A recurring WordPress security routine you can actually keep

For a busy small business owner, the difference is not just how long each WordPress security maintenance task takes, but how much of the security maintenance routine can be organized, explained, and safely prepared before you have to make a decision.

CadenceWhat you doRoughly how long manuallyRoughly how long with AI
WeeklyReview WordPress core, plugin, and theme updates. Apply low-risk updates, test complicated or business-critical plugins on staging first, confirm your latest backup exists, and check key pages or flows after updating.30 to 60 minutes5 to 15 minutes, plus any staging or manual checks
MonthlyCheck installed plugins and themes against what you actually use. Review users and roles, especially administrator accounts, and remove or downgrade access that is no longer needed.45 to 90 minutes10 to 20 minutes, depending on how many items need approval
QuarterlyIdentify inactive, redundant, abandoned, or confirmed-unused plugins and themes, then delete what you no longer need. Review WordPress security settings, backup settings, and connected services. Restore a backup somewhere safe to prove it works.2 to 4 hours30 to 60 minutes, plus the time needed to test the backup restore
Continuously, not by youFirewall, malware scanning, vulnerability monitoring, login protection, and automated backups run underneath all of the above.Handled by your tools and hostStill handled by your tools and host


These estimates assume someone who doesn’t already know every plugin, setting, and maintenance screen by heart. The AI Agent shortens the dashboard work by inventorying, explaining, grouping, and carrying out approved changes, but it doesn’t remove the time needed for staging, backup restores, or checking the parts of the site your visitors actually use.

Close the follow-through gap

WordPress security maintenance rarely fails because someone decides it doesn’t matter. It fails because it’s never the most urgent thing on any given day, and because a neglected site can look perfectly fine for months. That is the follow-through gap: the space between knowing what should be done and actually doing it regularly.

AI does not replace the security layers that run all the time. Your firewall, malware scanner, vulnerability monitoring, backups, and host still handle the continuous work. But an AI Agent can make the recurring WordPress-side work much easier to keep: checking updates, reviewing plugins and themes, auditing users, spotting old admin accounts, cleaning up clutter, and preparing changes for approval.

FAQs

Can AI keep a WordPress site secure?

No. AI cannot keep a WordPress site secure on its own. It can help with WordPress security maintenance that reduces risk, such as updates, audits, and access reviews, but firewall, malware scanning, vulnerability monitoring, and login protection still require dedicated security tools and your host.

What is included in WordPress security maintenance?

WordPress security maintenance includes updating WordPress, plugins, and themes, checking which extensions are installed, completing a WordPress user access audit, deleting unused plugins and themes, confirming backups ran, and checking your settings on a recurring schedule.

Does an AI Agent replace a firewall or WordPress security plugin?

No. An AI Agent does not replace a firewall or security plugin. They do different jobs. A firewall and scanner watch your site continuously, while an AI Agent helps you complete the maintenance work that would otherwise be postponed.

Why should unused WordPress plugins and themes be removed?

Unused WordPress plugins and themes should be removed because inactive code can still be attacked and still needs patching. Plugins accounted for 91% of WordPress vulnerabilities recorded in 2025, and switching a plugin off does not remove its code from your server.

How often should WordPress plugins and themes be updated?

WordPress plugins and themes should be updated at least weekly, and WordPress security updates for anything under active attack should be applied as soon as you can safely test them. Patchstack measured a weighted median of five hours between a flaw becoming public and the first attack on it.

Can an AI Agent update WordPress plugins safely?

Yes, with conditions. An AI Agent can update WordPress plugins safely when you back up first, test complicated plugins such as WooCommerce or page builders on a staging copy, and keep approval over high-impact changes rather than letting anything run unattended.

What is a safe recurring WordPress security routine?

A safe recurring WordPress security routine follows a WordPress security checklist: check updates and backups weekly, review users and installed extensions monthly, and check settings and remove unused plugins and themes quarterly, with dedicated security tools running continuously underneath.